France Hunts Fridge Hackers: 700 Stores Hit [2026]
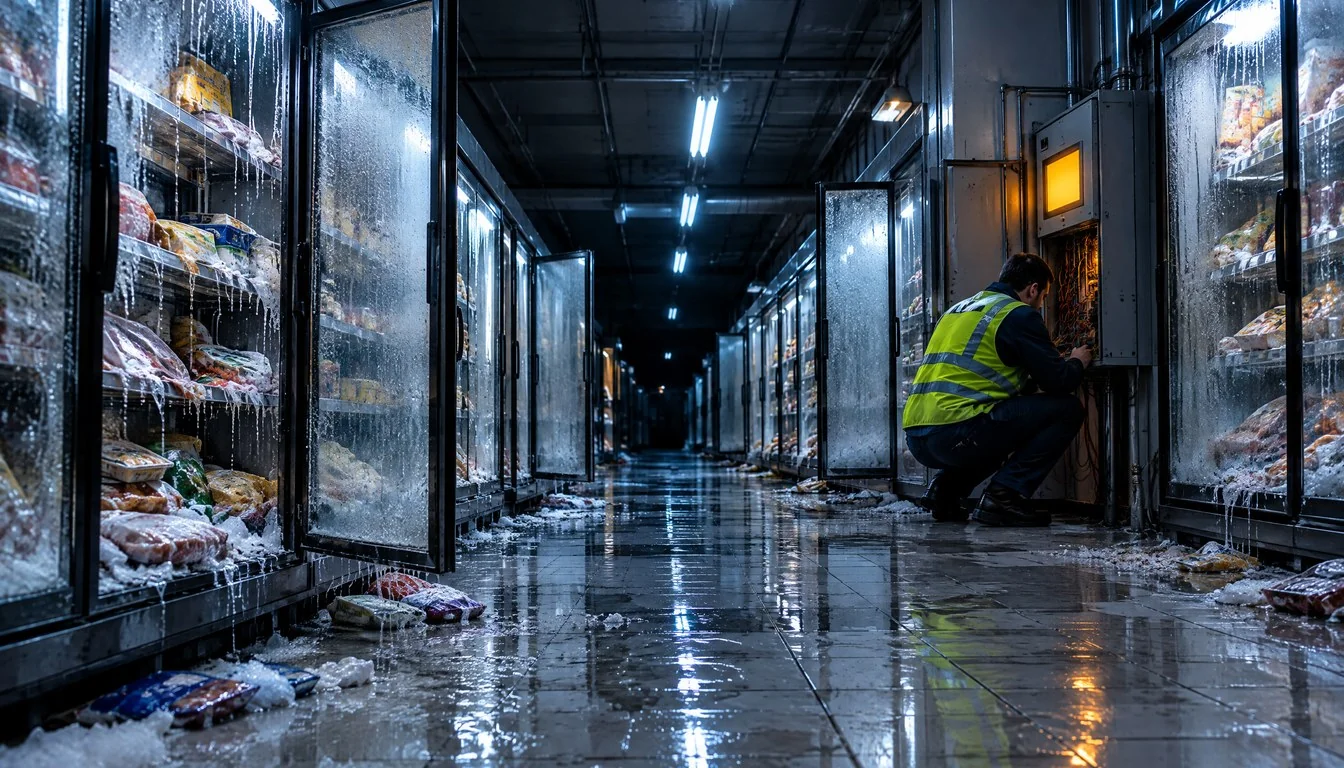
French investigators spent Tuesday chasing a trail that, as of October 15, 2026, still leads nowhere. No hacking group has stepped forward to claim the cyberattack that seized control of refrigeration systems at hundreds of supermarkets across France, and no ransom note has surfaced. What investigators do know is how it felt on the ground: freezers climbing toward 50 degrees Celsius, 122 Fahrenheit, while stock room sensors quietly recorded the damage before anyone on staff understood what was happening.
The french supermarket cyberattack hit cooling units tied to major chains including Carrefour, Monoprix, Intermarché and Coopérative U, according to reporting confirmed across multiple outlets. TrendinTech first covered the initial fridge shutdowns and fires as the story broke; this piece tracks what has changed since then: an active criminal probe, a national cybersecurity agency on the case, and still no attacker in sight. The Paris prosecutor’s office has opened a dedicated criminal probe, France’s national cybersecurity agency ANSSI has been brought in at the request of Prime Minister Sébastien Lecornu’s office, and the absence of a claim of responsibility is itself becoming part of the story.
Don't miss new tech stories on Google
Add TrendinTech once in the Google app and our stories appear in your news suggestions.
What Happened: A Cyberattack on France’s Cold Chain
The attack unfolded on October 13, 2026, when hackers seized control of cooling units at hundreds of supermarkets in a single coordinated push. French investigators have described the method only in general terms: whoever carried out the intrusion reached centralized systems that let store operators or vendors adjust fridge and freezer temperatures remotely, then used that access to force units toward 50 degrees Celsius instead of their normal operating range. The result was food spoilage across frozen and chilled sections, and in some locations, fires broke out as equipment overheated.
What makes this french supermarket cyberattack stand out from a typical data breach is the target. Nobody stole customer records or payment card numbers, at least not according to anything reported so far. Instead, the attackers appear to have gone straight for operational technology, the physical control systems that keep food cold, and flipped them against the retailers that depend on them. That distinction matters for how investigators, insurers and regulators are now treating the incident.
The Scale: 700 of France’s 10,000 Supermarkets
French Finance Minister Roland Lescure put a number on the damage during remarks to lawmakers, estimating that roughly 700 of France’s 10,000 supermarkets were affected. That figure, if it holds up under investigation, would make this one of the broadest single cyber incidents to hit the country’s retail sector in recent memory, measured by the sheer count of physical locations touched in one event.
Individual retailers have offered their own tallies. Intermarché said up to 200 of its stores were affected. Coopérative U reported almost 100 locations hit. Carrefour and Monoprix were both named among the affected chains in reporting from France 24, though neither has published a precise store count as of this writing. The gap between the finance minister’s nationwide estimate and the figures individual chains have confirmed suggests the full scope is still being assembled store by store.
| Retailer or Source | Stores Affected | Reported Detail |
|---|---|---|
| Nationwide estimate | About 700 of 10,000 stores | Cited by Finance Minister Roland Lescure |
| Intermarché | Up to 200 stores | Refrigeration systems forced to defrost |
| Coopérative U | Almost 100 locations | Refrigeration systems forced to defrost |
| Carrefour | Named as affected | Exact store count not yet published |
| Monoprix | Named as affected | Exact store count not yet published |
| Peak temperature reported | Up to 50°C (122°F) | Linked to food spoilage and fires |
Who Is Investigating: Paris Prosecutors and ANSSI
The Paris prosecutor’s office has opened a specific investigation into what it called the large-scale cyberattack affecting the refrigerators of several major food retail chains across France. Its stated goal, as reported by France 24, is to “identify the victims and establish the link with the damage they reported in terms of foodstuff losses and the outbreak of fires,” a formulation that signals prosecutors are treating this as a criminal matter with a defined set of harms to document, not just a technical incident for retailers to clean up on their own.
Running alongside the criminal probe is a technical one. ANSSI, France’s national cybersecurity agency, was tasked with investigating the attack at the direction of Prime Minister Sébastien Lecornu’s office. ANSSI’s involvement puts the incident in the same institutional lane as prior attacks on French critical infrastructure, and its findings, once published, are likely to shape how regulators across the European Union think about refrigeration and other operational technology tied to food retail.
Economy Minister Roland Lescure did not hold back in his public remarks. He called the targeting of equipment essential to France’s food supply “unacceptable” and said an investigation will be necessary to shed full light on this attack, a comment carried by AFP. Addressing French lawmakers, Lescure went further, describing the episode as a “wake-up call for everyone.”
No Claim, No Ransom: A Silence That Worries Experts
Three days after the attack began, nobody has stepped forward. No hacking group has publicly claimed responsibility, and no ransom demand has been reported by any of the affected retailers or by French authorities. That combination, disruption at scale with no financial ask and no public bragging, is unusual enough that it is shaping how security researchers are reading the incident.
A cybersecurity expert and former ANSSI employee identified as Aimé told CNN that “to our knowledge, no public claim of responsibility has been made,” a statement that underlines just how little is confirmed about who is behind the attack or why. Ransomware crews that disrupt physical infrastructure almost always want to get paid, and hacktivist groups that sabotage infrastructure almost always want credit. Neither pattern has shown up here, which leaves investigators weighing possibilities that range from a financially motivated actor still working up to a demand, to a less organized intrusion that got further than whoever triggered it expected. It is a similar puzzle to the one investigators faced after the Ledger hardware wallet theft earlier this year, where the scale of the loss outpaced any public attempt by the attacker to take credit.
French broadcaster BFM TV reported that hackers managed to remotely trigger the forced defrosting of refrigeration systems in numerous stores, language that points toward a shared control platform rather than dozens of separate, store-by-store break-ins. A person close to Prime Minister Lecornu was quoted suggesting ANSSI had identified a vulnerability tied to software from a Danish supplier, though that detail has not been confirmed by any named vendor and should be treated as unverified pending an official statement.
Why Refrigeration Systems Were a Soft Target
Modern supermarket refrigeration is rarely a standalone appliance plugged into a wall outlet. Most large chains run centralized building management platforms that monitor temperature, humidity and defrost cycles across dozens or hundreds of stores from one dashboard, often maintained by a third party rather than the retailer itself. That centralization is exactly what makes grocery refrigeration efficient to operate at scale, and it is exactly what turns a single compromised control point into a multiplier for an attacker.
Security researchers have warned for years that building management systems, the unglamorous category that covers HVAC, refrigeration and access control, tend to run on older software, get patched less often than customer-facing systems, and sit outside the budget and attention that retailers pour into protecting payment data. A fridge controller was never designed with the threat model of a nation-state or a ransomware crew in mind. This attack is a reminder that it now needs one.
Historical Context: Operational Technology Has Been a Target Before
This is not the first time attackers have gone after the physical systems behind a retail or infrastructure operation rather than its data. In 2013, intruders breached Target’s point of sale network after first compromising credentials belonging to an HVAC contractor, a case that is still cited in security training as the textbook example of a vendor side door into a retailer’s core systems. In 2016, the Mirai botnet hijacked hundreds of thousands of poorly secured internet of things devices, including routers and cameras, to launch denial of service attacks that knocked major sites offline. In 2021, a ransomware attack on Colonial Pipeline forced a shutdown of fuel delivery across the eastern United States, with the company paying roughly 4.4 million dollars to regain control before a portion was later recovered by US law enforcement.
What sets the French supermarket cyberattack apart is the target’s mundaneness. Pipelines and point of sale systems are obvious high value targets. A supermarket fridge is not, and that is precisely why so few retailers had invested in hardening it. Retail more broadly has had a rough stretch this year: the TFG cyberattack in London knocked three clothing brands offline, and a string of other breaches has kept cybersecurity teams at retail chains across Europe stretched thin.
| Year | Incident | Sector Targeted | Reported Outcome |
|---|---|---|---|
| 2013 | Target point of sale breach via HVAC vendor | Retail | Tens of millions of card accounts exposed |
| 2016 | Mirai IoT botnet | Connected devices | Hundreds of thousands of devices hijacked for DDoS attacks |
| 2021 | Colonial Pipeline ransomware | Energy infrastructure | Multi-day fuel shutdown, multi-million dollar ransom paid |
| 2026 | French supermarket fridge cyberattack | Retail refrigeration (OT) | About 700 stores affected, no ransom reported |
Market Impact: Retailers, Insurers and the Cold Chain
For Carrefour, Monoprix, Intermarché and Coopérative U, the immediate cost is measured in spoiled inventory and, in stores where fires broke out, physical repair bills. None of the four chains has published a financial estimate of losses tied to the french supermarket cyberattack, and the Paris prosecutor’s office has specifically said part of its job is to establish the link between the intrusion and the losses retailers reported, which suggests even the companies themselves are still totaling the damage.
The longer term cost will likely show up in insurance and capital spending. Cyber insurance policies written for retailers have historically focused on data breach liability, not physical property damage triggered by a digital intrusion. Insurers that cover French grocery chains are now almost certainly reassessing how operational technology risk gets priced, and refrigeration vendors and building management software suppliers should expect new questions from customers about patch cadence and remote access controls on the next renewal cycle, regardless of whether their own products were involved in this specific incident.
Competitive Comparison: How French Retailers’ Cyber Posture Stacks Up
France’s four largest grocery groups all run some version of centralized refrigeration monitoring, but they differ in how that infrastructure is owned and managed. Carrefour and Monoprix, both part of the same corporate family, tend to run more of their technology stack in house. Intermarché and Coopérative U operate through cooperative and franchise structures, where individual store owners have more autonomy but also more reliance on shared vendor platforms for things like refrigeration monitoring, which can mean a single vendor vulnerability has a wider blast radius across semi-independent locations.
That structural difference may help explain why Intermarché, with its network of independently owned stores leaning on shared systems, reported the highest single-chain store count among those that have published a figure. It is a pattern cybersecurity researchers have flagged in other sectors as well: franchise and cooperative business models that prize local ownership can end up sharing more technical plumbing than their organizational charts suggest, and that plumbing becomes the attacker’s actual target.
Regulatory Fallout: NIS2 and France’s Critical Infrastructure Rules
The European Union’s NIS2 directive, which expanded cybersecurity obligations to a wider range of sectors including parts of the food supply chain, was already pushing large retailers to document and secure their operational technology before this attack happened. France’s ANSSI has been the national enforcement body charged with translating that directive into domestic obligations. An incident of this scale, hitting food retail at a reported 700 locations with the Paris prosecutor’s office directly involved, gives ANSSI a concrete case study to point to the next time it pushes retailers toward faster compliance timelines.
Expect French and EU regulators to use this incident as use in ongoing conversations about extending stricter security requirements to building management and refrigeration vendors specifically, rather than leaving that category to fall under generic IT guidance that was written with office networks, not cold storage, in mind.
What Investigators Still Don’t Know
Several questions remain open as of October 15, 2026. Investigators have not publicly confirmed the exact method used to gain access to the refrigeration control systems. They have not confirmed the total financial cost of spoiled food and fire damage. They have not confirmed whether the same actor hit all 700 estimated locations in one operation or whether the attack unfolded through several separate intrusions that happened to surface around the same time. And they have not confirmed, officially, the reported detail about a vulnerability tied to a Danish software supplier, a claim that so far traces back to an unnamed person close to the prime minister’s office rather than to ANSSI or the vendor itself.
That list of unknowns is itself useful context. In most major ransomware or state linked attacks, some piece of attribution or financial motive becomes visible within the first 48 to 72 hours, either because the attacker wants to be known or because a ransom note forces the victim’s hand. The french supermarket cyberattack has now passed that window without either happening, which is part of why Lescure’s wake-up call framing has resonated with lawmakers and why ANSSI’s technical findings, whenever they are published, are likely to draw outsized attention.
What This Means for Retailers Outside France
US and global grocery chains run the same category of centralized refrigeration monitoring that French retailers do, often sourced from a small pool of international building management vendors. Nothing in the reporting so far indicates a US retailer was touched by this specific campaign, but the underlying lesson travels easily across borders: a vendor platform that controls cooling across hundreds of stores is a single point of failure, and most chains have not stress tested that platform the way they have tested their payment systems.
Retail security teams elsewhere should treat the french supermarket cyberattack as a prompt to inventory exactly which vendors have remote write access to refrigeration and HVAC controls, not just read access to monitoring dashboards, and to ask those vendors directly how a mass override would be detected and blocked in real time. Weak credential hygiene remains a common thread across unrelated incidents too. The recent Denmark breach that exposed 8.8 million records traced back in part to default or weak passwords, and the FBI’s arrest of a second ShinyHunters suspect this year showed how far stolen access can travel once it is in the wrong hands. Infrastructure attacks are not limited to IT either: the Starlink equipment fire in Poland is a reminder that physical and digital sabotage of connected infrastructure is becoming a recurring category across Europe, not an isolated event. Readers can track ongoing coverage of these cases in TrendinTech’s cybersecurity section.
Predictions: Where This Story Goes Next
- ANSSI will likely publish at least a partial technical summary of the intrusion method within weeks, given the scale of public and political attention Lescure’s remarks have generated.
- Expect at least one of the four named retailers to disclose a specific financial loss figure once insurance claims are filed, even if the company avoids a formal public statement beyond that filing.
- A claim of responsibility may still surface. Groups that stay quiet for several days sometimes resurface once they see how much media attention an attack generated, particularly if the goal was reputational rather than financial.
- Regulatory pressure under the EU’s NIS2 framework will likely tighten specifically around refrigeration and building management vendors serving food retailers, not just IT systems generally.
- Other European grocery chains outside France will likely conduct quiet, unannounced audits of their own refrigeration vendors in the coming weeks, whether or not they disclose doing so.
The Bigger Picture: Food Security Meets Cybersecurity
Roland Lescure’s choice of words, calling the attack a wake-up call, points at something larger than one bad week for four grocery chains. Food retail has spent the past decade digitizing supply chains, inventory tracking and now refrigeration, largely in the name of efficiency and waste reduction. Each layer of digitization has also added a layer of attack surface that nobody budgeted security resources to match. The french supermarket cyberattack did not touch a single customer’s wallet, yet it still managed to spoil food, trigger fires and pull in national prosecutors and the country’s top cybersecurity agency within 48 hours.
That is the part of this story likely to outlast the headlines about any single attacker’s identity. Whoever is eventually found responsible, or if nobody ever is, the exposure that let it happen will still need fixing across an entire industry that has spent far more time thinking about card skimmers than thermostats.
Frequently Asked Questions
What happened in the French supermarket cyberattack?
Hackers seized control of refrigeration systems at hundreds of French supermarkets on October 13, 2026, forcing fridge and freezer temperatures up to 50 degrees Celsius, which spoiled food and in some cases sparked fires.
How many stores were affected?
French Finance Minister Roland Lescure estimated about 700 of France’s 10,000 supermarkets were affected. Intermarché reported up to 200 of its stores hit, and Coopérative U reported almost 100 locations affected.
Which retailers were named in the attack?
Carrefour, Monoprix, Intermarché and Coopérative U were all named in reporting on the incident.
Has anyone claimed responsibility?
No. As of October 15, 2026, no individual or group has publicly claimed responsibility for the attack, and no ransom demand has been reported.
Who is investigating the attack?
The Paris prosecutor’s office has opened a criminal investigation, and ANSSI, France’s national cybersecurity agency, is conducting a technical investigation at the request of Prime Minister Sébastien Lecornu’s office.
How did hackers reach the refrigeration systems?
Investigators have not officially confirmed the exact method. French broadcaster BFM TV reported that hackers remotely triggered forced defrosting across numerous stores, pointing to a centralized control platform rather than individual break-ins at each location.
Was a specific software vulnerability confirmed?
A person close to the prime minister’s office was quoted suggesting a vulnerability tied to a Danish software supplier was involved, but this has not been confirmed by ANSSI or by any named vendor, so it remains unverified.
Could a similar attack hit retailers outside France?
Nothing reported so far indicates retailers outside France were affected by this specific campaign, but security researchers note that centralized refrigeration and building management platforms are common across the global grocery industry, making the underlying vulnerability class relevant well beyond France.
Related Coverage
Rachel Kowalski
Rachel Kowalski is the Cybersecurity Analyst at TrendinTech, where she covers vulnerabilities, ransomware, supply chain attacks, nation-state operations and the security rules shaping organizations in the United States and Europe. She writes to make risks and countermeasures understandable to people who are not specialists.
All stories by Rachel Kowalski (240)