Ledger Hack Drains $86M, CZ Warns Crypto Holders [2026]
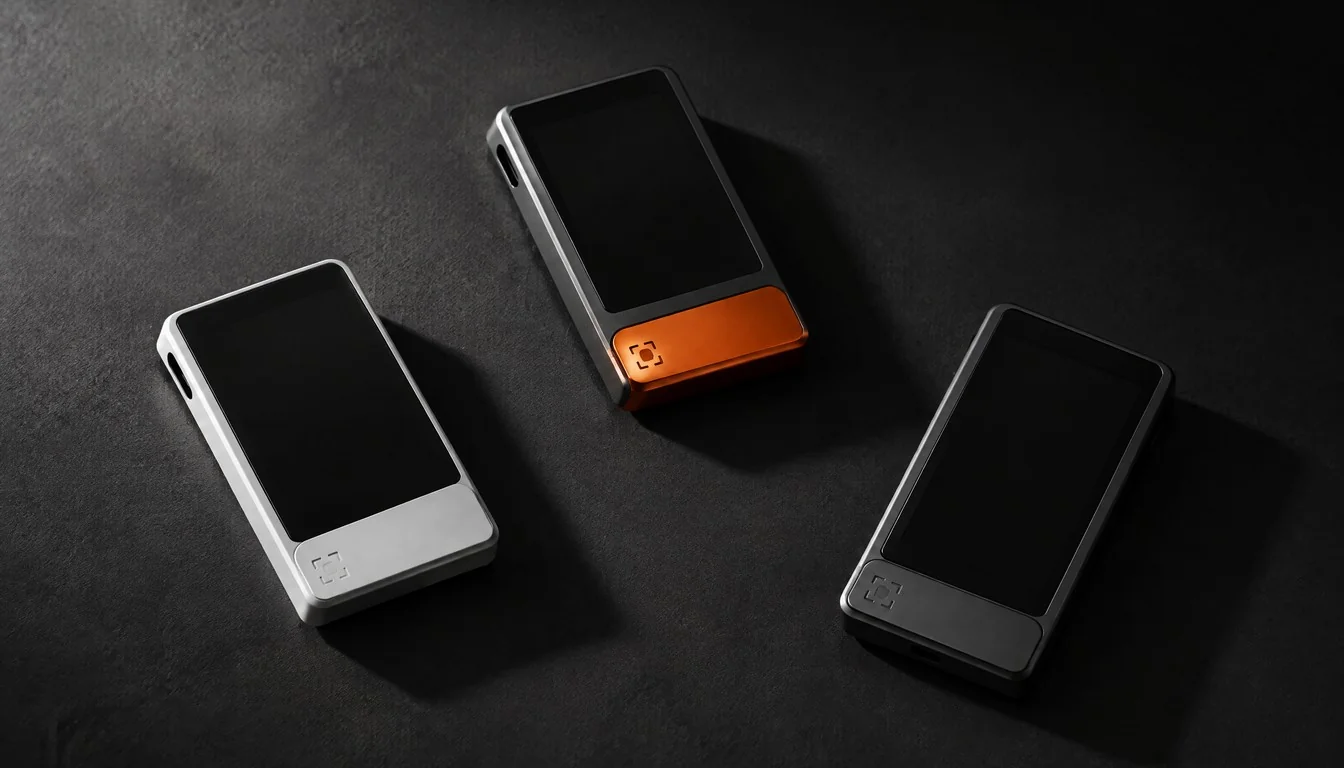
Binance co-founder Changpeng Zhao is urging crypto holders to reassess how they store their coins after hardware wallet maker Ledger confirmed it is investigating reports of stolen funds tied to devices sold through a Southeast Asia reseller. The warning, issued October 12, 2026, lands on top of a separate, still-disputed hardware wallet security incident involving Coldcard devices, giving the crypto industry two fresh reminders that owning your private keys does not automatically mean they are safe.
On-chain investigator Specter has pegged losses from the Ledger-linked incident at more than $86 million, spread across Bitcoin, Ethereum, and TRON wallets, according to reporting from Cointribune. Ledger itself has not confirmed that figure, and the company says the exact loss total, the number of affected customers, and the precise mechanism behind the thefts are all still undetermined. That has not stopped the story from dominating crypto security conversations this week, especially once Zhao weighed in publicly on what he believes happened.
Don't miss new tech stories on Google
Add TrendinTech once in the Google app and our stories appear in your news suggestions.
What Happened: The $86 Million Ledger-Linked Theft
According to Hodl.press, Ledger launched a formal investigation after a wave of reports surfaced from users who had purchased hardware wallets through CryptoBilis, a reseller operating in Southeast Asia. The pattern described by affected users is consistent across most reports: a device bought from this specific seller, followed weeks or months later by funds draining out of wallets that the owner believed were secure in cold storage.
Specter’s on-chain tracing suggests the theft touched wallets holding Bitcoin, Ethereum, and TRON, with combined losses exceeding $86 million. Ledger has acknowledged the reports and opened an investigation but has stopped short of validating that number, noting that the full scope of affected customers is still being worked out. That gap between the on-chain estimate and the official company position is important context for anyone following this story: the headline number driving most coverage right now is an outside estimate, not a confirmed internal tally.
Reporting from TMGM narrows the reseller’s location to Malaysia, and indicates Ledger suspended sales through CryptoBilis while the investigation into the roughly $86 million in losses continues. That suspension is a telling signal on its own: a hardware wallet manufacturer does not typically cut off an authorized distribution channel unless it sees enough internal evidence to treat the reseller as a liability, even before a cause is confirmed publicly.
Who Is CryptoBilis and How a Device Resale Chain Becomes a Security Risk
CryptoBilis is described in multiple reports as a third-party reseller of Ledger hardware wallets in Southeast Asia, rather than Ledger’s own direct sales channel. That distinction matters because it defines where, in theory, a breach of trust could have occurred. A hardware wallet is only as secure as every link in the chain that gets it from the factory to the buyer’s hands sealed and untouched. Once a device passes through an intermediary reseller, that chain gains an extra link, and extra links are exactly where supply-chain attacks tend to surface.
CoinMarketCap reports that Ledger is investigating drained wallets connected specifically to customers who bought through this reseller, with on-chain analysis pointing to hundreds of wallets affected and losses above $86 million. Importantly, reports describing the units as counterfeit or tampered with remain unconfirmed by Ledger. The company has not said publicly whether the devices sold through CryptoBilis were genuine hardware that was intercepted and modified, outright counterfeits built to mimic a real Ledger device, or something else entirely. Until Ledger publishes findings, any claim about the exact mechanism should be treated as a working theory rather than an established fact.
Why Reseller-Based Attacks Are Hard to Detect Early
A tampered hardware wallet does not necessarily behave differently at setup. If an attacker pre-generates a seed phrase, swaps a chip, or otherwise interferes with how a device creates its private keys, the owner can use the wallet normally for weeks or months with zero visible symptoms. The theft only becomes obvious once the attacker decides to move funds, by which point the victim has long since trusted the device with meaningful holdings. That lag between compromise and visible loss is precisely what makes supply-chain attacks against hardware wallets so dangerous, and so difficult to pin down after the fact.
Changpeng Zhao’s Warning to Crypto Holders
Zhao, widely known by his initials CZ and recognized as a Binance co-founder, addressed the incident directly, framing it as likely limited in scope rather than evidence of a flaw in Ledger’s hardware itself. “Based on the available information, this appears localized to a supply chain attack involving a single seller. A small number of people probably bought fake Ledger devices (or tampered Ledger devices),” Zhao said, according to reporting cited by Benzinga.
Zhao also called for a coordinated industry response to help victims recover whatever funds can still be traced. “I expect and know all BNB ecosystem players (and all industry) to help trace and recover the funds,” he said. That statement positions the incident as a shared problem for the broader crypto ecosystem rather than one company’s isolated customer-service matter, and it puts pressure on exchanges and blockchain analytics firms to cooperate on tracing stolen assets as they move across chains.
Zhao’s framing is notable for what it does not say. He did not claim Ledger’s core hardware or firmware is compromised at scale, and he did not confirm the $86 million figure. Instead, he offered a measured read: a likely single bad actor exploiting one weak link in distribution, affecting a limited subset of buyers. Whether that assessment holds up once Ledger completes its own investigation remains an open question, and crypto holders reading his comments should treat them as an informed outside opinion, not a verified conclusion from the manufacturer.
The Coldcard Exploit: A Second, Separate Hardware Wallet Scare in 2026
The Ledger-linked case is not the only hardware wallet security story shaping headlines this year. Reporting from Cryptonews.com.au covers a separate incident involving Coldcard devices, where attackers drained Bitcoin from wallets generated with defective firmware. That reporting describes at least 15 separate attackers pulling funds from roughly 7,300 addresses, with a confirmed tally of 1,596 BTC at the time of that report, a figure some outlets price at more than $100 million.
Other coverage of the same underlying Coldcard issue cites a larger figure of 1,700 BTC, valued at $141.82 million at the prices used in that report. The gap between 1,596 BTC and 1,700 BTC, and between “more than $100 million” and “$141.82 million,” comes down to when each outlet took its snapshot and which bitcoin price it applied. Neither figure has been consolidated into one officially confirmed loss total, so readers should treat the Coldcard numbers as a range rather than a single hard figure, bounded by the lower confirmed tally and the higher estimate tied to peak bitcoin pricing.
What ties the two incidents together in this week’s coverage is not a shared cause. They are different devices, different manufacturers, and reportedly different root issues (a reseller-side supply-chain concern for Ledger-linked devices versus defective firmware for Coldcard units). What they share is a conclusion: hardware wallets marketed as the gold standard for self-custody are still producing eight-figure and nine-figure losses in 2026, years after the category was supposed to have solved the custodial-exchange-hack problem.
Comparing the Two 2026 Hardware Wallet Incidents
| Detail | Ledger-linked / CryptoBilis incident | Coldcard firmware incident |
|---|---|---|
| Reported loss estimate | More than $86 million (Specter, on-chain estimate) | 1,596–1,700 BTC, roughly $100M–$141.82M depending on pricing used |
| Confirmed by manufacturer | No — Ledger investigating, scope undetermined | No single officially confirmed total across reports |
| Suspected root cause | Possible supply-chain attack tied to one reseller (CryptoBilis) | Defective or vulnerable firmware, per reporting |
| Assets affected | Bitcoin, Ethereum, TRON | Bitcoin |
| Number of attackers identified | Not specified in current reporting | At least 15 separate attackers, per Galaxy Research–cited reporting |
| Addresses affected | Hundreds of wallets, per on-chain analysis | Roughly 7,300 addresses |
| Public response | Ledger suspended sales through the reseller; CZ issued public warning | Ongoing attacker activity reported as tally expanded |
Historical Context: Hardware Wallets Were Supposed to Be the Safe Option
Hardware wallets built their reputation on a simple pitch: keep private keys on an offline device that never touches the internet, and exchange-style hacks become irrelevant. That pitch held up well against remote attackers for years, which is part of why devices from Ledger, Trezor, and Coldcard became the default recommendation for anyone holding meaningful crypto outside an exchange. The weakness that keeps resurfacing is not the offline design itself, it is everything around it: the manufacturing process, the distribution chain, the firmware update pipeline, and the reseller network that gets a sealed box into a buyer’s hands.
This pattern is not new to 2026. Security researchers have warned for years that counterfeit or tampered hardware wallets circulating through unofficial or loosely vetted resellers represent one of the most realistic attack paths against self-custody, precisely because the attack happens before the victim ever interacts with the blockchain. What makes the current cluster of incidents notable is the scale: two separate nine-figure-adjacent loss events in the same year, against two different well-known hardware wallet brands, within months of each other.
The broader crypto theft picture backs up why this keeps happening. Blockchain analytics firm Chainalysis reported that more than $2.17 billion was stolen from cryptocurrency services in the first half of 2025 alone, and personal-wallet compromises accounted for 23.35% of stolen-fund activity in that period, according to the firm’s 2025 Crypto Crime Mid-Year Update. Wallet-level theft, as opposed to exchange hacks, is already a meaningful chunk of the total losses industry-wide, and incidents like the Ledger-linked case and the Coldcard exploit sit squarely inside that category.
Why the Loss Figures Keep Shifting
Both incidents illustrate a recurring reporting problem with crypto theft stories: the dollar value attached to a hack is rarely fixed. On-chain investigators typically tally stolen coins first, then convert to a dollar figure using whatever price snapshot is available at the time of their report. Because bitcoin and ether prices move constantly, two outlets reporting on the same stolen-coin total days apart can publish meaningfully different dollar figures, which is exactly why the Coldcard numbers range from roughly $100 million to $141.82 million depending on the source.
Market Impact: What This Means for Investor Confidence
Hardware wallet makers sell trust as much as they sell hardware. A buyer pays a premium for a Ledger, Trezor, or Coldcard device specifically because they are trying to remove themselves from exchange-counterparty risk. When headlines connect a well-known brand name to an eight-figure theft, even one attributed to a third-party reseller rather than the manufacturer’s own factory, the reputational exposure lands on the brand regardless of where the fault ultimately sits. That is the central tension Ledger now has to manage: its own direct-sale hardware may be entirely unaffected, but “Ledger” is the name attached to every headline about this story.
For everyday crypto holders, the practical market impact shows up less in token prices and more in buying behavior. Expect increased scrutiny of where hardware wallets are purchased, more demand for devices bought directly from manufacturer websites rather than third-party marketplaces, and renewed interest in verification steps at setup. Crypto holders who have historically treated a sealed box as proof of authenticity are being reminded, again, that packaging alone does not guarantee a clean supply chain.
There is also a trust-cost angle for the reseller ecosystem broadly. Authorized resellers exist because they expand a hardware wallet maker’s reach into markets the company cannot serve directly and efficiently. If incidents like this one erode confidence in third-party resellers as a category, manufacturers may face pressure to tighten reseller vetting, publish authorized-seller lists more prominently, or push harder toward direct-only sales, each of which comes with its own cost and reach trade-offs.
Self-Custody vs. Centralized Exchange Security: The Trade-Offs Resurface
Every time a hardware wallet incident makes headlines, it reopens the long-running debate about whether self-custody or centralized exchange custody is actually the safer default for most users. Neither path is risk-free, and the Ledger-linked incident is a useful case study in why the answer depends heavily on how disciplined the user is about the supply chain, not just the technology.
| Risk factor | Self-custody hardware wallet | Centralized exchange |
|---|---|---|
| Primary attack surface | Device supply chain, firmware, physical theft of seed phrase | Exchange’s own servers, insider access, hot wallet breaches |
| Counterparty risk | Minimal once genuine device is verified | User depends entirely on exchange solvency and security practices |
| Recovery options if compromised | Limited; funds move on-chain and may be unrecoverable | Varies; some exchanges have reimbursed users after breaches |
| Verification burden | Falls on the individual buyer at purchase and setup | Falls on the exchange’s internal security team |
| Typical failure mode in 2026 incidents | Tampered or counterfeit device from unofficial reseller | Not applicable to this story’s incidents |
Pew Research Center data offers a sense of scale for how many people are navigating these trade-offs at all: approximately 17% of U.S. adults have ever invested in or used cryptocurrency, while 8% used it in the previous year, according to a Pew Research survey reported by NBC News. That is a meaningful population of retail holders who, realistically, are not running independent security audits on every device they buy, which is exactly why reseller-level attacks can scale before anyone notices a pattern.
Competitive Landscape: How Ledger, Trezor, and Coldcard Compare on Supply-Chain Security
Ledger has long marketed a secure chip architecture and an official buy-direct channel as its core defense against counterfeiting, alongside device-authenticity checks performed through its companion app at setup. The CryptoBilis-linked incident, if confirmed as a reseller-side compromise, would not necessarily indict that architecture, it would indict the specific distribution path a subset of buyers used. Trezor has taken a different design approach historically, emphasizing open-source firmware that outside researchers can audit, which proponents argue reduces the risk of hidden backdoors but does not eliminate supply-chain tampering risk on its own. Coldcard has built its reputation around an air-gapped, Bitcoin-only design aimed at advanced users, and the firmware-based exploit described in this year’s reporting suggests that even a narrower, security-focused hardware design is not immune to implementation bugs that attackers can find and exploit at scale.
None of the three brands’ current incidents, as reported, point to a single unifying design flaw across the category. Instead, each case reinforces a different lesson: Ledger’s situation underscores reseller and distribution-chain risk, while the Coldcard case underscores firmware-quality risk. For a buyer deciding which hardware wallet to trust, the practical takeaway is less about picking a “safer” brand and more about controlling the variables within reach: buying only from a manufacturer’s direct store, verifying device authenticity at setup, and keeping firmware updated through official channels only.
How This Compares to Other Recent Crypto and Cybersecurity Incidents
This story is landing in a year already crowded with supply-chain-adjacent security failures across tech broadly. Law enforcement has continued chasing data-theft groups tied to large-scale breaches, including the FBI’s arrest of a second ShinyHunters suspect tied to stolen agent data, and European regulators have widened sanctions aimed squarely at tech supply chains, with the EU’s 1,600 Russia-linked sanctions targeting chips and drones. Both cases, like the Ledger-linked theft, trace back to a weak point somewhere outside the core product itself: a reseller, a vendor, a logistics chain.
Crypto-specific extortion has also been a running theme this year, visible in the ongoing Cyberleek group’s $30 million crypto ransom threat tied to leaked GTA 6 footage. That case and the Ledger-linked theft are different in almost every detail, but both reflect the same underlying trend: criminal groups increasingly treat crypto, whether stolen from wallets directly or demanded as ransom, as the preferred payout mechanism for large-scale digital crime in 2026.
What Crypto Holders Should Do Right Now
Security researchers and exchange executives responding to this incident have converged on a familiar but newly urgent checklist for anyone holding crypto on a hardware wallet, particularly one not purchased directly from the manufacturer.
Hardware wallet security checklist (post-incident):
1. Confirm your device was purchased directly from the
   manufacturer's official store, not a third-party reseller.
2. Re-verify device authenticity using the manufacturer's
   official companion app, not a link from an email or ad.
3. If you bought through any reseller (including CryptoBilis
   or any unverified Southeast Asia distributor), move funds
   to a freshly purchased, directly-sourced device.
4. Never reuse a seed phrase that was generated on a device
   of uncertain origin -- generate a brand-new seed on a
   verified device and transfer funds to new addresses.
5. Check firmware update history; only apply updates signed
   and distributed through official manufacturer channels.
6. Split large holdings across multiple wallets/devices
   rather than concentrating funds in a single hardware unit.
Password hygiene and account separation matter just as much as the hardware itself. Readers who have not already locked down the accounts tied to their exchange logins and recovery emails should treat this as a prompt to do so, and tools covered in our best password manager setup guide or a self-hosted Vaultwarden deployment are reasonable starting points for anyone who has been putting off that cleanup.
Predictions: Where Hardware Wallet Security Goes From Here
- Manufacturer-direct sales push. Expect Ledger and competing brands to more aggressively steer buyers toward direct-only purchasing in marketing and setup flows, reducing reliance on third-party resellers in regions where counterfeiting risk is highest.
- Reseller audits and certification programs. Hardware wallet makers will likely roll out stricter authorized-reseller vetting or public “verified seller” lists following this incident, similar to how other electronics categories responded to counterfeiting waves.
- Slower, more public incident disclosures. Given how much scrutiny Ledger is facing for not yet confirming the $86 million figure, expect hardware wallet makers generally to move toward faster, more detailed public updates during active investigations to control the narrative gap that outside estimates currently fill.
- Increased firmware audit demands. The Coldcard firmware issue will likely push the hardware wallet industry toward more frequent third-party security audits of firmware, particularly for brands marketing themselves on security-first design.
- Industry-wide tracing cooperation. Zhao’s public call for “all BNB ecosystem players (and all industry)” to help trace stolen funds signals a trend toward exchanges and analytics firms coordinating faster on freezing or flagging wallets tied to confirmed thefts, regardless of which brand’s hardware was involved.
What We Still Don’t Know
It is worth being direct about the limits of current reporting. Ledger has not confirmed the $86 million loss figure, has not confirmed how many customers are affected, and has not confirmed whether the devices sold through CryptoBilis were counterfeit, tampered with after leaving the factory, or compromised some other way. The Coldcard figures remain a range rather than a single confirmed total, split between a lower bound tied to confirmed BTC amounts and a higher estimate dependent on which bitcoin price snapshot is applied. Readers should expect these numbers to shift, possibly significantly, once Ledger publishes formal findings.
What is already clear is the shape of the problem: a trusted hardware brand, a third-party sales channel, and a gap in oversight somewhere in between that cost real users real money. That combination has shown up before in the hardware wallet space, and this week’s events make clear it has not been fully solved yet.
Frequently Asked Questions
What exactly happened with Ledger and the $86 million theft?
Ledger is investigating reports that more than $86 million was stolen from users who bought hardware wallets through CryptoBilis, a reseller operating in Southeast Asia. The loss figure comes from on-chain investigator Specter and has not been confirmed by Ledger.
Is my Ledger device affected if I bought it directly from Ledger?
Current reporting ties the incident specifically to devices purchased through the CryptoBilis reseller. Devices purchased directly from Ledger’s official store are not implicated in the reporting reviewed for this article, though Ledger’s investigation is still ongoing.
What did Changpeng Zhao (CZ) say about the incident?
Zhao said the available information suggests the incident is localized to a supply-chain attack involving a single seller, and that a small number of people probably bought fake or tampered Ledger devices. He also called on exchanges and the broader crypto industry to help trace and recover stolen funds.
Is the Coldcard exploit the same incident as the Ledger theft?
No. They are separate incidents involving different manufacturers. The Coldcard case involves funds drained from wallets tied to defective firmware, with reported losses ranging between roughly $100 million and $141.82 million depending on the bitcoin count and price used. The Ledger-linked case involves a reseller supply-chain concern and more than $86 million in reported losses.
How can I check if my hardware wallet is genuine?
Use the manufacturer’s official companion app to run its built-in authenticity check, and confirm your purchase came from the manufacturer’s direct store or a listed authorized reseller. If you bought from an unverified third party, security researchers recommend transferring funds to a newly purchased, directly-sourced device using a freshly generated seed phrase.
Should I move my crypto to an exchange instead of a hardware wallet?
Both options carry different risks. Hardware wallets remove exchange-counterparty risk but place the burden of supply-chain verification on the buyer. Exchanges remove that verification burden but introduce dependence on the exchange’s own security and solvency. Neither this incident nor broader 2025–2026 data suggests one option is categorically safer; they fail in different ways.
How common are hardware wallet and self-custody thefts?
Personal-wallet compromises accounted for 23.35% of stolen-fund activity in crypto during the first half of 2025, according to Chainalysis, out of more than $2.17 billion stolen from cryptocurrency services industry-wide in that period. Wallet-level theft is already a significant share of total crypto crime losses.
Has Ledger said when it will release final findings?
No firm timeline has been reported. Ledger has confirmed it is investigating and has suspended sales through the CryptoBilis reseller, but has not published a confirmed final loss total, affected-customer count, or root-cause determination as of this writing.
Related Coverage
Rachel Kowalski
Rachel Kowalski is the Cybersecurity Analyst at TrendinTech, where she covers vulnerabilities, ransomware, supply chain attacks, nation-state operations and the security rules shaping organizations in the United States and Europe. Before moving into journalism she worked as a threat intelligence analyst at a security vendor and later reported for CyberScoop and the security desk at Wired, covering the SolarWinds compromise and the ransomware wave that hit hospitals and pipelines. Rachel holds a Master of Science in Cybersecurity from the Georgia Institute of Technology and attends Black Hat and DEF CON in Las Vegas each year, where she follows research from the security community. She writes to make risks and countermeasures understandable to people who are not specialists.
All stories by Rachel Kowalski (236)