FBI Arrests 2nd ShinyHunters Suspect, Agent Data Hit [2026]
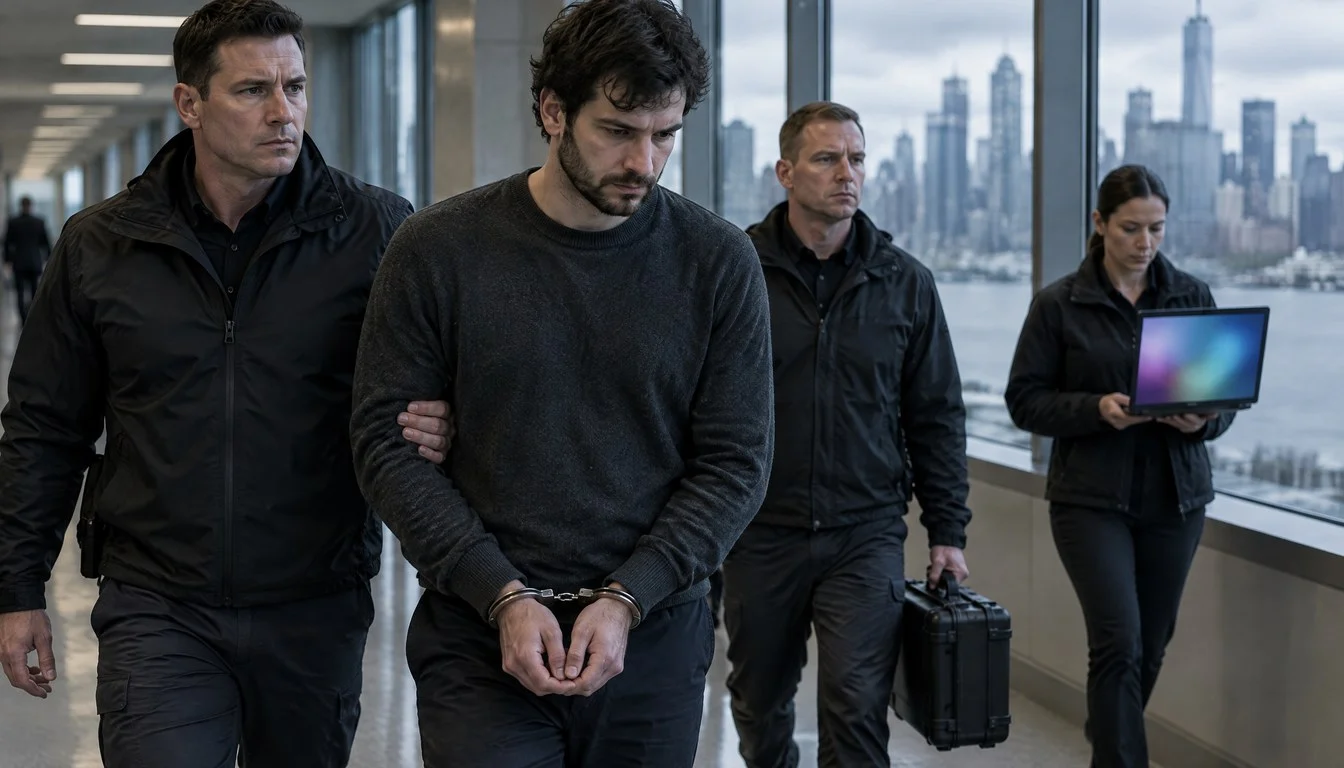
The FBI confirmed on Friday, October 9, 2026, that its agents arrested a second suspected member of the ShinyHunters hacking collective tied to a breach of the agency’s own personnel data. The suspect, identified as Canadian national Edward Dubrovsky, was taken into custody in the Philadelphia area of Pennsylvania, according to CNN. Federal authorities now consider him a primary co-conspirator in the intrusion that exposed personal information belonging to thousands of current and former FBI employees.
The arrest marks one of the more pointed law enforcement responses yet to the ShinyHunters campaign, a loosely affiliated extortion crew that has spent much of 2026 hammering corporate and government targets alike. For a bureau whose entire mission rests on securing sensitive information, having its own jobs portal turned into an attack surface is an uncomfortable irony, and it has pushed the FBI ShinyHunters arrest story to the top of cybersecurity headlines this week.
Don't miss new tech stories on Google
Add TrendinTech once in the Google app and our stories appear in your news suggestions.
What Happened: The FBIjobs.gov Breach, Explained
According to the FBI’s own account, the target was not an internal bureau system but a recruiting-facing jobs website, commonly referenced as FBIjobs.gov, that is reportedly managed by a third-party vendor rather than hosted directly on federal infrastructure. That detail matters. It places this incident squarely inside a pattern that has defined 2026’s worst breaches: attackers increasingly skip the hardened front door of a target organization and instead go after the software vendors, staffing portals, and SaaS platforms that sit just outside the perimeter but still hold real data.
FBI Director Kash Patel tied the incident directly to ShinyHunters, saying the group is believed to be responsible for the recent FBIjobs.gov incident. The data exposed reportedly includes personal and sensitive information concerning thousands of current and former FBI employees, a category of data that is unusually valuable on criminal marketplaces because it can be leveraged for everything from identity theft to targeted social-engineering attacks against federal personnel. The exact number of affected employees and the precise volume of stolen data have not been disclosed in the reporting available so far, and readers should treat any specific figure circulating online as unconfirmed until the bureau or Justice Department releases an official count. Outlets including CBS News have covered the arrest as part of the wider ShinyHunters enforcement story.
Who Is Edward Dubrovsky?
Edward Dubrovsky is a Canadian national who, per CNN’s reporting, appeared in federal court in the Philadelphia area on Thursday, October 8, 2026, a day before the FBI’s public confirmation of the arrest. A magistrate judge appointed him a federal public defender, standard procedure for a defendant who has not yet secured private counsel. Beyond the fact of the arrest and his alleged affiliation with ShinyHunters, the public record is thin. The exact criminal charges against Dubrovsky have not been established in available reporting, and nothing in the current coverage indicates a conviction, plea, or admission of guilt. He is, at this stage, a suspect facing allegations, not a convicted hacker, and this article treats his legal status accordingly.
What federal authorities have said is that they view Dubrovsky as a primary co-conspirator in the attack on FBI data, a characterization that suggests investigators believe he played a central operational role rather than a peripheral one. That framing is significant for anyone tracking how the Justice Department builds cases against distributed hacking crews: naming someone a primary co-conspirator typically signals prosecutors have assembled evidence linking a specific individual to specific infrastructure, communications, or stolen data, rather than simply associating them with a loosely defined online handle.
ShinyHunters: A Group With a Long Rap Sheet
ShinyHunters did not appear out of nowhere. The name has circulated in cybersecurity circles for several years, typically associated with large-scale data theft followed by extortion attempts rather than ransomware encryption. The group’s modus operandi tends to favor exploiting third-party cloud platforms, abusing stolen credentials, and social-engineering help desks to gain access, then threatening to leak or sell stolen records unless a ransom is paid. That approach distinguishes ShinyHunters from encryption-first ransomware gangs, and it is part of why the FBIjobs.gov incident fits a recognizable pattern rather than looking like a novel attack technique. Security news outlet BleepingComputer has tracked the group’s shifting tactics across multiple campaigns in recent years.
Law enforcement pressure on the group has been building for months. Dutch authorities had already arrested one of the alleged leaders of ShinyHunters prior to this latest action, according to CNN’s reporting. Taken together with Friday’s arrest, that makes at least two publicly confirmed law enforcement actions against individuals tied to the group within a relatively short window, suggesting international investigators have made real progress mapping the collective’s membership and infrastructure, even as the group’s broader network likely remains active.
Kash Patel’s Statement and the FBI’s Public Response
FBI Director Kash Patel addressed the arrest directly, framing it as continued momentum against the group rather than a one-off win. According to CNN, Patel said, “Earlier this week, our agents in the field arrested another suspected co-conspirator,” a statement that both confirms the arrest and implicitly acknowledges this is not the first individual linked to the group that federal agents have pursued. Patel also connected the arrest to the FBIjobs.gov incident specifically, reinforcing that the bureau views this as part of a continuing investigation rather than a closed case.
The choice to publicize the arrest so quickly, within a day of Dubrovsky’s court appearance, also reflects a broader shift in how federal agencies communicate about cybercrime enforcement. Rather than waiting for an indictment to be unsealed or a trial date to be set, agencies increasingly announce arrests early, partly to reassure stakeholders, including the thousands of employees whose data may have been exposed, that an active response is underway, and partly to signal to other members of extortion crews that law enforcement is closing in.
A Timeline of the Investigation So Far
Piecing together the public reporting, the sequence of events looks like this:
[Prior]      ShinyHunters-linked intrusion targets FBIjobs.gov,
             a third-party-managed FBI recruiting portal.
[Prior]      Dutch authorities arrest one alleged ShinyHunters leader.
2026-10-08   Edward Dubrovsky appears in federal court near Philadelphia;
             a magistrate judge appoints a federal public defender.
2026-10-09   FBI Director Kash Patel publicly confirms the arrest of
             "another suspected co-conspirator" of ShinyHunters.
[Ongoing]    Exact charges, affected-employee count, and data volume
             remain undisclosed pending further DOJ/FBI statements.
That timeline underscores how much of this story is still unfolding. Several of the most commonly asked questions, including how many records were taken and what specific statutes Dubrovsky is accused of violating, simply are not answered in the public record yet. Readers should expect additional detail to surface as the case proceeds through federal court in Pennsylvania.
Why a Breach of FBI Employee Data Is Different
Not all data breaches carry equal weight, and a breach touching current and former FBI personnel sits in a different risk category than, say, a retail loyalty-program leak. Federal law enforcement employees are themselves targets for foreign intelligence services, criminal organizations, and domestic extremists, which means exposure of their personal details, even relatively mundane fields like home addresses, phone numbers, or employment history, carries a security dimension that goes beyond ordinary identity-theft risk. It can inform physical-security threats, enable impersonation in social-engineering attempts against other agencies, or simply erode the operational anonymity that undercover and support personnel depend on.
That is part of why this story resonates well beyond the cybersecurity trade press. It is also why organizations tracking federal cybersecurity incidents, including teams that follow guidance published through the FBI’s Internet Crime Complaint Center, tend to treat any breach touching law enforcement personnel data as a higher-priority event than its raw record count might otherwise suggest.
Historical Context: Government Data Breaches Before This One
The FBIjobs.gov incident is far from the first time a federal system, or a vendor serving one, has been compromised. The table below places it alongside several of the most consequential U.S. government-linked breaches of the past decade for context on scale and impact. Note that the FBIjobs.gov record count is listed as unconfirmed, consistent with the current state of public reporting, while the other figures reflect previously disclosed, widely reported totals.
| Incident | Year | Entity Affected | Reported Scale | Primary Vector |
|---|---|---|---|---|
| OPM personnel records breach | 2015 | U.S. Office of Personnel Management | Approx. 21.5 million records (per OPM disclosure) | Network intrusion, suspected state-linked actors |
| SolarWinds supply-chain compromise | 2020 | Multiple U.S. federal agencies | Dozens of agencies/companies affected | Trojanized software update |
| Colonial Pipeline ransomware incident | 2021 | Critical infrastructure operator | Pipeline shutdown, multi-day disruption | Compromised VPN credential |
| MGM Resorts intrusion | 2023 | MGM Resorts International | Days of operational outages | Help-desk social engineering (Scattered Spider) |
| Change Healthcare ransomware incident | 2024 | UnitedHealth Group subsidiary | Nationwide claims-processing disruption | Compromised remote-access credential |
| FBIjobs.gov / ShinyHunters incident | 2026 | FBI recruiting portal (third-party managed) | Unconfirmed; described as thousands of employee records | Alleged third-party vendor compromise |
The pattern across nearly every row is the same: attackers rarely need to breach the hardest, most hardened core of a target. They go through the vendor, the update pipeline, or the help desk instead. The FBIjobs.gov incident, with its reported link to a third-party vendor, fits neatly into that decade-long trend rather than representing a new kind of attack.
ShinyHunters in Context: How It Compares to Other Major Hacking Collectives
ShinyHunters is one of several extortion-focused groups that have dominated cybersecurity headlines over the past few years. Understanding how it compares to its closest peers helps explain why the FBI treats arrests tied to the group as significant wins, and why security teams continue to rate third-party and identity-based attacks as a top-tier risk heading into 2027 budget planning.
| Group | Primary Tactic | Notable Targeting Pattern | Law Enforcement Action to Date |
|---|---|---|---|
| ShinyHunters | Data theft and extortion, often via third-party platform abuse | Corporate databases, SaaS tenants, now a federal recruiting portal | Dutch arrest of an alleged leader; FBI arrest of Edward Dubrovsky as a second suspected co-conspirator |
| Scattered Spider | Help-desk social engineering, SIM swapping | Casinos, telecoms, retail, insurance | Multiple arrests reported across the US and UK in prior cases |
| LAPSUS$ | Credential theft, insider recruitment | Large tech firms, source-code repositories | Arrests of alleged teenage members in the UK and Brazil in prior cases |
| ALPHV/BlackCat | Ransomware-as-a-service, double extortion | Healthcare, finance, critical infrastructure | FBI-led infrastructure disruption in a prior law enforcement operation |
| Cl0p | Mass exploitation of file-transfer software flaws | Large enterprises via shared vulnerable software | Ongoing international investigations in prior cases |
What stands out is that nearly every group on this list has, at some point, been described as loosely organized, decentralized, and difficult to fully dismantle through a single arrest. ShinyHunters appears to follow the same structure, which is precisely why federal officials have been careful to describe Dubrovsky as a co-conspirator rather than the group’s sole operator. Dismantling a collective like this typically requires a string of arrests across multiple jurisdictions over an extended period, not a single decisive raid.
The Third-Party Vendor Problem Keeps Repeating Itself
If there is a single structural lesson repeated across the FBIjobs.gov incident and the historical breaches listed above, it is that outsourcing a system does not outsource the risk. Government agencies, like most large enterprises, rely heavily on third-party vendors to run recruiting portals, benefits systems, and other non-core applications. Security teams have pushed vendor-risk management up the priority list for years, yet incidents involving managed platforms keep recurring because vendor security posture is inherently harder to audit and enforce than an organization’s own internal controls.
This is also where tooling matters. Teams trying to keep pace with disclosed vulnerabilities across their vendor ecosystem increasingly lean on structured patch-prioritization workflows that cross-reference the CISA Known Exploited Vulnerabilities catalog against active scanning results, rather than trying to track every advisory manually. The FBIjobs.gov incident is a reminder of why that discipline extends beyond an organization’s own servers and into every vendor contract it signs.
Market and Industry Impact
Breaches involving federal law enforcement data tend to move faster through procurement and policy channels than breaches at private companies, simply because the political pressure to respond is immediate and bipartisan. Expect heightened scrutiny of vendor contracts across federal agencies in the weeks following this disclosure, particularly contracts tied to recruiting, HR, and benefits platforms that touch personnel records but are not always classified as mission-critical systems requiring the highest security tier.
For the cybersecurity vendor market, incidents like this one tend to reinforce demand for identity verification, vendor risk monitoring, and managed detection services, categories that have already seen strong enterprise spending growth through 2026. Security leaders evaluating their own exposure to this kind of third-party risk are also the same audience increasingly comparing credential-management tools built around phishing-resistant authentication, since weak or reused credentials remain one of the most common entry points attackers exploit when going after a vendor-managed portal rather than a hardened core network.
There is also a quieter infrastructure angle worth noting. As more government-adjacent systems move to vendor-run cloud platforms, the security posture of the underlying cloud and serverless infrastructure becomes part of the attack surface too, a dynamic that has pushed agencies and contractors to scrutinize how workloads are deployed and isolated, an area where comparisons of serverless platform security and access controls increasingly factor into procurement decisions.
What Happens Next for Edward Dubrovsky
With a federal public defender now appointed, Dubrovsky’s case will proceed through the standard federal criminal process: likely a detention hearing, a preliminary or grand jury determination on formal charges, and eventually an arraignment if an indictment is returned. None of the available reporting indicates what specific charges prosecutors intend to bring, and it is worth repeating that nothing in the current record establishes guilt. The Justice Department has not released charging documents publicly as of this writing, according to the sources reviewed for this piece, so specifics about statutes, potential penalties, or a trial timeline remain unknown.
What is clearer is the symbolic weight of the case. A successful prosecution tied to an attack on the FBI’s own data would be a notable deterrence signal to other ShinyHunters-affiliated actors, reinforcing that targeting federal systems, even indirectly through a vendor, invites a different tier of investigative resources than targeting a private company might.
Expert Reaction
FBI Director Kash Patel’s own public comment remains the most direct, verified statement available on the arrest. Speaking about the operation, Patel said: “Earlier this week, our agents in the field arrested another suspected co-conspirator,” a remark that frames the Dubrovsky arrest as part of a continuing campaign against ShinyHunters rather than an isolated success, according to CNN’s reporting on the arrest. Independent threat-intelligence teams, including researchers who track extortion groups for firms like Google’s Threat Intelligence Group, have separately noted that groups following ShinyHunters’ playbook tend to persist operationally even after individual members are arrested, since the collective’s infrastructure and recruitment channels are often distributed across many, loosely coordinated participants.
Predictions: Where This Story Goes From Here
- Expect the Justice Department to unseal formal charges against Edward Dubrovsky within weeks, likely including conspiracy and computer-fraud counts consistent with prior ShinyHunters-linked prosecutions, though the exact statutes remain unconfirmed for now.
- Additional arrests tied to ShinyHunters are likely in 2026 and 2027, following the same pattern seen with Scattered Spider and LAPSUS$, where law enforcement action comes in waves rather than a single takedown.
- Federal agencies will likely face renewed congressional questions about vendor oversight for HR and recruiting platforms, potentially accelerating stricter security requirements in future government contracts.
- The FBI will probably disclose a more specific count of affected employees once its internal review concludes, though no timeline for that disclosure has been given.
- Expect cybersecurity vendors serving government clients to use this incident in marketing around third-party risk management and identity security products through the remainder of 2026.
How This Fits the Broader 2026 Breach Landscape
2026 has already seen a steady drumbeat of extortion-driven breaches across sectors, and government targets have not been spared. What makes the FBIjobs.gov case distinct is less the technical sophistication, which appears consistent with ShinyHunters’ established playbook of targeting externally managed platforms, and more the symbolism of the FBI itself being on the receiving end. Security teams inside other federal agencies and their contractors are almost certainly reviewing their own vendor-managed HR and recruiting systems this week as a direct result of this disclosure, a reactive pattern that tends to follow any breach involving a recognizable, high-profile victim.
It is also worth noting how this story intersects with the broader AI-driven shift in both offense and defense. As threat actors increasingly automate reconnaissance and phishing content generation, defenders are leaning more heavily on automated triage tools, an arms race dynamic visible even in unrelated corners of the industry, such as the kind of automated scoring and decision systems discussed in coverage of Microsoft’s newer AI decision-scoring tools, which illustrates how quickly automation is being adopted on the defensive side of enterprise security operations as well.
What Current and Former FBI Employees Should Do
For anyone who believes they may be among the current or former FBI employees whose data was exposed, the standard post-breach precautions apply even before an official notification arrives. That includes monitoring financial accounts and credit reports for unusual activity, being alert to unsolicited phone calls or emails referencing employment at the bureau, and enabling multi-factor authentication on personal accounts wherever it is not already active. Given that the exact scope of the breach has not been confirmed, erring on the side of caution is reasonable even for employees who have not received a direct notification.
Security researchers also generally advise against engaging with anyone claiming to represent ShinyHunters or offering to “verify” exposure in exchange for personal information, a common secondary tactic extortion groups use to harvest additional data from anxious breach victims.
Frequently Asked Questions
Who was arrested in connection with the FBI data breach?
Edward Dubrovsky, a Canadian national, was arrested in the Philadelphia area of Pennsylvania. Federal authorities describe him as a primary co-conspirator linked to the ShinyHunters hacking group.
When was the arrest announced?
The FBI confirmed the arrest publicly on Friday, October 9, 2026. CNN reported that Dubrovsky had appeared in federal court a day earlier, on Thursday, October 8, 2026.
What was actually breached?
Reports indicate the target was an FBI jobs website, commonly referred to as FBIjobs.gov, that is managed by a third-party vendor. The incident reportedly exposed personal and sensitive information belonging to thousands of current and former FBI employees, though an exact figure has not been officially confirmed.
Is Edward Dubrovsky the leader of ShinyHunters?
No. Available reporting describes him as a suspected co-conspirator, not the group’s leader. Dutch authorities previously arrested a different individual described as one of the alleged leaders of ShinyHunters.
Has Edward Dubrovsky been convicted?
No. As of this reporting, Dubrovsky has only been arrested and appeared in federal court, where a public defender was appointed. The exact charges against him have not been established in available public reporting, and he has not been convicted of any crime.
What is ShinyHunters known for?
ShinyHunters is a hacking collective generally associated with large-scale data theft and extortion, frequently by targeting third-party cloud platforms and vendor-managed systems rather than breaching hardened internal networks directly.
How many FBI employees were affected?
The exact number has not been disclosed. Reporting describes the exposure as affecting thousands of current and former FBI employees, without a precise confirmed figure.
What should affected employees do now?
Security experts generally recommend monitoring financial and credit accounts for unusual activity, enabling multi-factor authentication on personal accounts, and treating unsolicited communications referencing FBI employment with caution, even before receiving official notification of exposure.
Related Coverage
Rachel Kowalski
Rachel Kowalski is the Cybersecurity Analyst at TrendinTech, where she covers vulnerabilities, ransomware, supply chain attacks, nation-state operations and the security rules shaping organizations in the United States and Europe. Before moving into journalism she worked as a threat intelligence analyst at a security vendor and later reported for CyberScoop and the security desk at Wired, covering the SolarWinds compromise and the ransomware wave that hit hospitals and pipelines. Rachel holds a Master of Science in Cybersecurity from the Georgia Institute of Technology and attends Black Hat and DEF CON in Las Vegas each year, where she follows research from the security community. She writes to make risks and countermeasures understandable to people who are not specialists.
All stories by Rachel Kowalski (232)