French Supermarket Fridges Hacked to 50°C, Food Lost [2026]
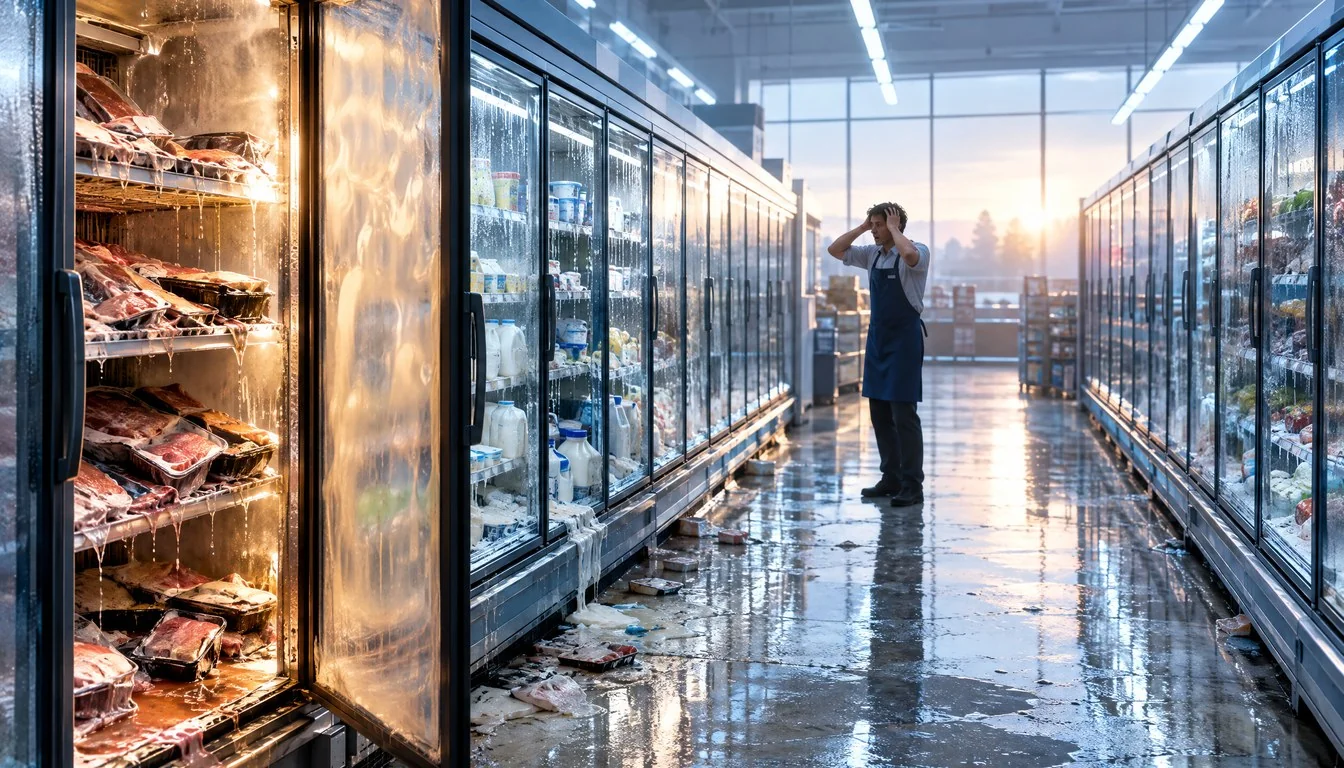
Hundreds of supermarkets across France woke up on Monday, October 12, 2026, to spoiled meat, melted ice cream and, in some cases, small fires, after hackers remotely seized control of connected refrigeration systems overnight. The Paris prosecutor’s office confirmed it has opened an investigation into what it called a “large-scale cyberattack affecting the refrigerators of several major food retail chains across France,” according to CBS News.
The attack did not touch payment systems, customer data, or point-of-sale networks. It targeted something far more mundane and, it turns out, far more exposed: the internet-connected controllers that keep supermarket fridges and freezers cold. By forcing those controllers into defrost mode, attackers pushed refrigerator temperatures up to 50°C (122°F), according to Reuters. The result was hundreds of stores quietly cooking their own cold chain while employees slept.
Don't miss new tech stories on Google
Add TrendinTech once in the Google app and our stories appear in your news suggestions.
What happened overnight in France
The timeline, as pieced together from statements by the affected retailers, points to a coordinated overnight operation. Les Mousquetaires, the group behind Intermarché, told reporters that refrigerators at roughly 150 of its stores were heated to 50°C for about six hours overnight, a window long enough to compromise an entire inventory of fresh and frozen goods, as reported by Reuters. A separate report put the number of affected Intermarché shops as high as 150 to 200, suggesting the scale of the intrusion was still being tallied well into Monday.
Carrefour, France’s largest retail chain, said 80 of its supermarkets were hit. The company was quick to note that the vast majority of its roughly 6,000 stores nationwide were untouched, framing the incident as contained rather than catastrophic for its network as a whole, according to Reuters and CBS News. Monoprix reported that 5% of its stores were affected, a smaller but still notable slice of its footprint. Coopérative U said almost 100 of its outlets were reportedly targeted, rounding out a list of at least four major French grocery brands caught up in the same overnight event.
Taken together, the affected store count across Intermarché, Carrefour, Monoprix and Coopérative U runs into the several hundreds, matching the Paris prosecutor’s office’s own description of a “large-scale” attack. No single company has disclosed a precise, verified nationwide total, and the exact combined figure remains part of the active investigation.
Timeline of the overnight attack
Based on statements from the affected chains, the attack unfolded overnight between Sunday and Monday, October 12, 2026. Les Mousquetaires described a roughly six-hour window during which Intermarché refrigerators were held at 50°C before staff arrived and discovered the damage in the morning. Carrefour, Monoprix and Coopérative U have not published their own precise start-and-end times, but all three confirmed impacts consistent with the same overnight period. By Monday morning, the Paris prosecutor’s office had confirmed the attack and opened a formal investigation, a fast turnaround that suggests the scale of simultaneous reports from multiple chains made the incident impossible to treat as an isolated equipment failure.
How hackers turned refrigerators into a weapon
Modern supermarket refrigeration is not a dumb appliance plugged into a wall socket. It is a networked system: compressors, sensors and defrost cycles are coordinated by internet-connected controllers that let a chain’s facilities team monitor every store’s cold chain from a central dashboard, flag failures before food spoils, and schedule routine defrost cycles that clear frost buildup from evaporator coils. That remote-management convenience is exactly what made the systems vulnerable. Attackers did not need to break into individual stores. They needed to reach the software that tells refrigerators when to defrost, and then simply tell every connected unit to do it at once, for hours, in the middle of the night when nobody was there to notice the alarm.
Danfoss, a major supplier of refrigeration controls used in commercial food retail, said the affected stores in France were running outdated firmware, and added that it had long advised customers to keep supported systems updated with the latest firmware. That statement points to a familiar culprit in industrial control system security: a known, patchable weakness that sat unaddressed on live production equipment for long enough to be exploited at scale. It echoes a pattern security researchers have flagged for years in building-automation and refrigeration monitoring networks, where uptime pressure and a “if it’s not broken, don’t touch it” mentality routinely delay firmware updates on equipment that was never designed with today’s threat model in mind.
The defrost cycle itself is the mechanism that makes this attack so disruptive. A normal defrost cycle runs for a limited time, under thermostatic limits, specifically to avoid raising food-contact surfaces above safe thresholds. Forcing that cycle to run unsupervised for roughly six hours, as Les Mousquetaires described, removes every one of those safety limits. Refrigerated compartments built to hold food at 4°C or lower were instead pushed toward 50°C, a temperature range where bacterial growth accelerates and food safety guidelines consider product unsafe for consumption within a matter of hours, not the full overnight window attackers achieved.
The financial and food-safety fallout
Every affected retailer that has spoken publicly has confirmed the same outcome: the food had to go. Intermarché said affected branches would have to “throw away all of the products” that were fresh and frozen, according to Reuters and Le Monde. A Les Mousquetaires spokesperson separately confirmed that all affected food had been discarded specifically to eliminate health risks, rather than attempting to salvage any portion of inventory that may have only been partially compromised.
That is a meaningful operational and financial hit. A single mid-size supermarket’s fresh and frozen inventory, from meat and dairy to prepared foods and ice cream, typically represents a large share of daily perishable stock value. Multiply that across 150 Intermarché stores, 80 Carrefour locations, around 100 Coopérative U outlets and a slice of Monoprix’s network, and the total loss is substantial even before factoring in the separate damage the Paris prosecutor’s office is investigating: reported fires. The prosecutor’s office said the investigation would establish the connection between the attack and reported food losses and fires, meaning officials have not yet confirmed exactly how overheating refrigeration units escalated into actual fire incidents, only that both outcomes are under formal review.
No retailer or official body has published a confirmed, audited total euro figure for the damage. Reports have characterized the losses as potentially worth millions of euros, but that remains an unconfirmed estimate rather than an official tally. Expect that number to firm up as insurers, the affected chains and investigators complete damage assessments over the coming days and weeks.
| Retailer | Reported stores affected | Context |
|---|---|---|
| Intermarché / Les Mousquetaires | ~150 stores (one estimate: 150–200) | Fridges heated to 50°C for about six hours overnight |
| Carrefour | 80 stores | Vast majority of ~6,000 total stores unaffected |
| Coopérative U | Almost 100 outlets | Reportedly targeted in the same overnight window |
| Monoprix | 5% of stores | Smaller but still measurable share of network hit |
Why connected refrigeration became an attack surface
Retail refrigeration sits at an uncomfortable intersection of operational technology and corporate IT. For decades these systems ran in isolation: a technician visited each store, checked gauges, and manually logged temperatures. Over the past decade, chains rolled out centralized monitoring to cut labor costs, catch failures before they caused spoilage, and feed energy-efficiency programs with real-time data. That shift moved refrigeration control onto IP networks, often supplied and maintained by third-party vendors rather than the retailer’s own cybersecurity team.
The France incident fits a pattern security teams have watched build for years across operational technology: critical physical infrastructure, from HVAC to refrigeration to building access control, increasingly runs on commodity networking and firmware that does not get the same patch cadence as a corporate laptop fleet. Readers who have followed recent coverage of Yandex’s data center disruptions will recognize the broader theme: critical digital infrastructure, whether a data center or a supermarket’s cold chain, is only as resilient as its weakest, least-monitored component. In this case, that component was a refrigeration controller running software that Danfoss says was out of date.
This is also not the first time attackers have targeted operational technology in retail or critical infrastructure settings this year. Regulators across the European Union have spent much of 2026 tightening tech supply chain scrutiny, including an expanded sanctions package targeting chips and hardware tied to Russia, covered in detail in our report on the EU’s 1,600 Russia sanctions. Whether this attack has any connection to state-linked actors or sanctioned supply chains is, as of publication, entirely unconfirmed. The identity and motive of the attacker have not been established, and investigators have given no public indication of attribution.
Historical context: industrial control systems under fire
Attacks on operational technology are not new, but attacks that hit ordinary retail infrastructure at this scale, affecting consumer-facing food safety rather than factory production lines or power grids, are a newer and more visible category. Security researchers have warned for years that building-management systems, including refrigeration, HVAC and access control, often ship with default credentials, rarely get patched after installation, and are frequently exposed to the internet far more broadly than operators realize. The France incident gives that warning a concrete, grocery-aisle face: ruined meat, discarded frozen goods and reported fires, rather than an abstract vulnerability scan finding.
It also lands in a year when European retailers and infrastructure operators have already faced a string of high-profile cybersecurity incidents, from credential-theft campaigns detailed in our coverage of the FBI’s ShinyHunters arrest to patch-management pressure covered in our CVE patch pipeline tutorial. The common thread across all of these stories is the same: attackers are increasingly going after the unglamorous, unpatched systems that keep physical operations running, not just the databases that hold customer records.
Market and industry impact
For France’s grocery sector, the immediate impact is operational: discarded inventory, emergency restocking, and almost certainly a wave of internal firmware audits across every chain that uses networked refrigeration hardware, regardless of whether they were hit this time. Industrial refrigeration and building-automation vendors, Danfoss among them, are likely to see a short-term surge in firmware update requests and security consulting engagements as retailers scramble to confirm their own systems are not running the same outdated software blamed for the France incident.
There is also a reputational dimension. Carrefour’s decision to publicly stress that the “vast majority” of its roughly 6,000 stores were unaffected is a textbook crisis-communications move: contain the narrative before a four-figure percentage sounds worse than a double-digit store count. Expect similar statements from other affected chains in the days ahead, alongside expected pressure from French regulators and possibly EU-level cybersecurity bodies for a public accounting of what went wrong and when the vulnerable firmware was first flagged.
Insurance is the other market to watch. Cyber-insurance policies covering physical property damage and spoilage, rather than just data-breach liability, are a relatively young product line in Europe. A confirmed, multi-million-euro claim tied to a single coordinated cyberattack on refrigeration infrastructure would be a significant test case for how those policies are underwritten and priced going forward.
Competitive comparison: how the major French chains responded
Each affected retailer’s public posture offers a small window into its crisis response, even this early. Les Mousquetaires was the most forthcoming with a specific, unambiguous duration: roughly six hours of forced defrost overnight, plus a clear statement that it discarded all affected product to eliminate health risk. Carrefour emphasized scale and containment, highlighting that its 80 affected stores were a small fraction of its roughly 6,000-store network. Monoprix offered a percentage rather than a raw store count, and Coopérative U’s figure of almost 100 outlets came through a secondary report rather than a direct company statement at the time of writing.
| Company | Public response style | Key disclosed detail |
|---|---|---|
| Les Mousquetaires / Intermarché | Direct, detailed | ~150 stores, 50°C for ~6 hours overnight, food discarded |
| Carrefour | Containment-focused | 80 of ~6,000 stores affected |
| Monoprix | Proportional disclosure | 5% of stores affected |
| Coopérative U | Reported, not yet confirmed directly | Almost 100 outlets reportedly targeted |
What the investigation still needs to answer
The Paris prosecutor’s office has confirmed the attack happened and opened a formal investigation, but several core questions remain open. Who carried out the attack, and why, has not been established. How the attackers gained access to refrigeration controllers across at least four separate retail chains in a single overnight window, whether through a shared vendor, a shared software platform, or independent exploitation of similar outdated firmware at each company, has not been detailed publicly. And the exact mechanism connecting forced defrost cycles to the reported fires is still under review rather than confirmed.
Investigators will also need to determine whether this was an opportunistic attack against known-vulnerable, internet-exposed equipment, or a more deliberate, targeted campaign against French food retail specifically. The fact that multiple competing chains were hit on the same night suggests either a shared point of failure in the supply chain for refrigeration monitoring software, or a broad scanning campaign that simply found and exploited whichever vulnerable systems it could reach.
Predictions: where this story goes next
- Expect French and EU cybersecurity authorities to push for mandatory firmware update and reporting requirements for operational technology vendors serving critical retail and food infrastructure, building on the same regulatory momentum behind this year’s expanded sanctions on tech supply chains.
- Danfoss and competing refrigeration-control vendors will likely face pointed questions from retail customers worldwide, not just in France, about which installed systems are still running unpatched firmware.
- Other major European grocery chains outside France will almost certainly run emergency audits of their own refrigeration networks in the coming weeks, even if they were not directly affected.
- A confirmed euro figure for total losses, covering spoiled inventory and fire damage, will likely emerge within the investigation’s early findings, though it may take weeks given the number of chains and stores involved.
- This incident will likely become a reference case in future reporting whenever industrial control system or operational technology vulnerabilities in retail, logistics, or food supply chains make headlines again.
Lessons for IT and security teams beyond retail
For technology and security professionals outside the grocery sector, the France incident is a useful reminder that operational technology deserves the same patch discipline as any internet-facing server. Refrigeration controllers, HVAC systems, and other building-automation hardware increasingly run on standard networking protocols and, in many cases, standard operating systems underneath vendor-specific firmware. That means they inherit the same vulnerability classes as any other connected device, but they often sit outside the normal vulnerability-management pipeline that IT teams use for laptops, servers, and cloud workloads.
Teams managing their own patch and vulnerability pipelines may find it useful to review how structured, prioritized patching frameworks work, such as the approach outlined in our best password manager setup walkthrough, which covers locking down the credentials guarding administrative dashboards in the first place. The same discipline that keeps a cloud fleet patched against known exploited vulnerabilities applies just as directly to refrigeration controllers, elevator systems, and every other piece of connected hardware operating quietly in the background of a physical retail footprint. Organizations serious about credential hygiene across both IT and OT environments may also want to look at options like our self-hosted Vaultwarden walkthrough as part of a broader push to lock down administrative access to vendor dashboards and remote-management consoles, the exact kind of system that appears to have been exploited in this attack.
FAQ: France supermarket refrigeration cyberattack
What exactly happened to French supermarket refrigerators?
Hackers remotely forced connected refrigeration systems into defrost mode overnight, pushing fridge and freezer temperatures up to 50°C (122°F) at stores across several major French retail chains, according to Reuters.
Which supermarket chains were affected?
Intermarché (Les Mousquetaires), Carrefour, Monoprix and Coopérative U all reported impacts. Intermarché said about 150 stores were hit, Carrefour said 80 stores, Coopérative U said almost 100 outlets, and Monoprix said 5% of its stores were affected.
Did the attack cause fires?
The Paris prosecutor’s office said the investigation would establish the connection between the attack and reported food losses and fires. Fires have been reported, but the exact mechanism linking them to the forced defrost cycles has not yet been officially confirmed.
How much food and money was lost?
Affected retailers confirmed that fresh and frozen food at impacted stores was discarded to eliminate health risks. No official, audited total euro figure has been published; reports describe potential losses in the millions of euros, but that remains unconfirmed.
Who is responsible for the attack?
The identity and motive of the attacker have not been established. This remains an open part of the Paris prosecutor’s office’s investigation.
Why were refrigerators vulnerable to hacking in the first place?
Danfoss, a major refrigeration-control supplier, said affected stores in France were running outdated firmware, and noted it had long advised customers to keep supported systems updated. Outdated firmware on internet-connected industrial control systems is a well-documented attack vector.
Is my local supermarket at risk of something similar?
Any retailer using internet-connected refrigeration or building-automation systems with unpatched firmware carries similar exposure. The France incident is likely to accelerate firmware audits at grocery chains well beyond the companies directly affected.
Is this related to other recent attacks on digital infrastructure in Europe?
No confirmed link has been established to other 2026 incidents, including drone strikes on data centers or EU sanctions targeting tech supply chains. Investigators have not disclosed any attribution connecting this attack to a specific actor or campaign.
Related Coverage
Rachel Kowalski
Rachel Kowalski is the Cybersecurity Analyst at TrendinTech, where she covers vulnerabilities, ransomware, supply chain attacks, nation-state operations and the security rules shaping organizations in the United States and Europe. Before moving into journalism she worked as a threat intelligence analyst at a security vendor and later reported for CyberScoop and the security desk at Wired, covering the SolarWinds compromise and the ransomware wave that hit hospitals and pipelines. Rachel holds a Master of Science in Cybersecurity from the Georgia Institute of Technology and attends Black Hat and DEF CON in Las Vegas each year, where she follows research from the security community. She writes to make risks and countermeasures understandable to people who are not specialists.
All stories by Rachel Kowalski (236)