IMF Warns on AI Cyberattacks, Cites 50°C Fridge Hack [2026]
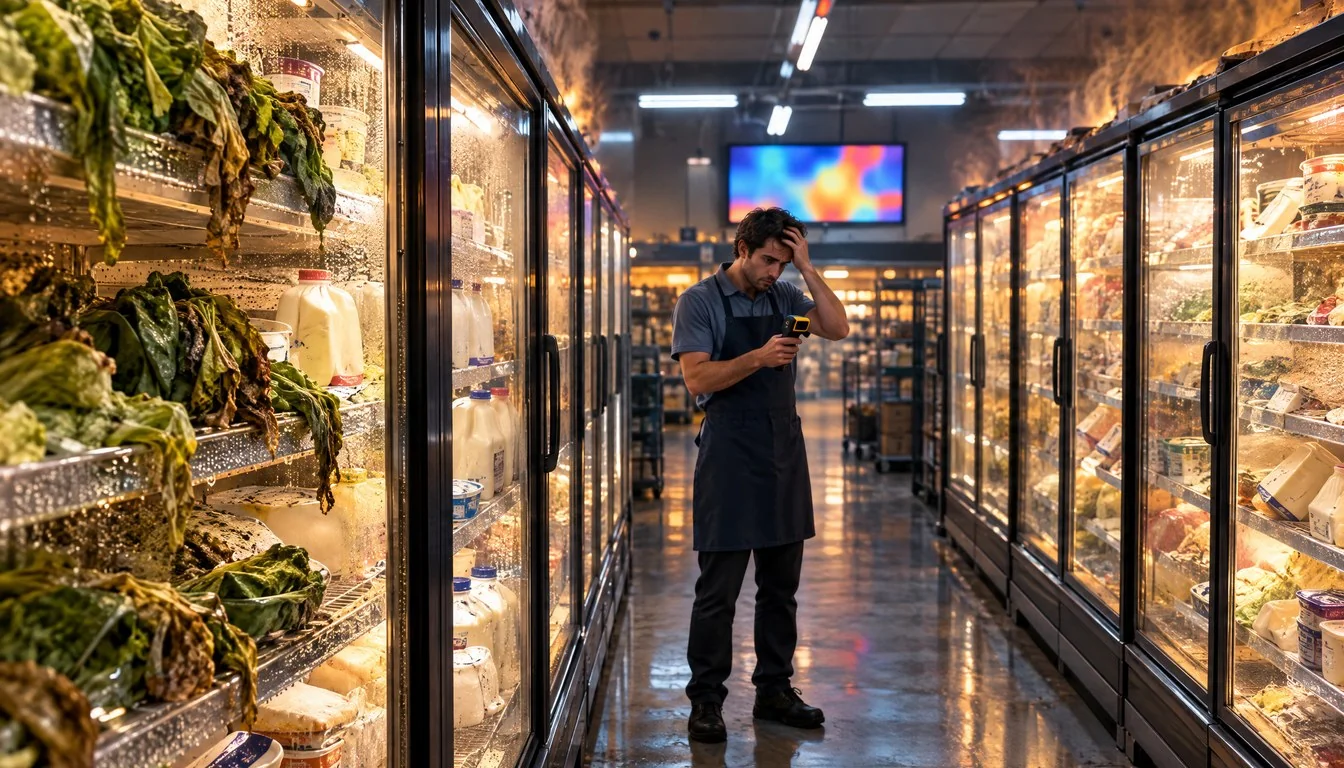
The International Monetary Fund used its biggest stage of the year to deliver an unusual warning: the next shock to the global financial system might not start in a boardroom or a bond market. It might start in a supermarket fridge.
Speaking at the IMF-World Bank Annual Meetings in Bangkok, Kristalina Georgieva, managing director of the International Monetary Fund, told finance ministers, central bankers and economists gathered in the Thai capital that artificial intelligence is already reshaping the threat that cyberattacks pose to the world economy. Her reference point was not a bank heist or a stock exchange outage. It was a refrigeration breach in France that pushed supermarket cooling units to roughly 50 degrees Celsius, spoiling food and forcing retailers to throw out stock, according to reporting aggregated by outlets including World News Network and the cybersecurity news tracker sternit.de, which collects coverage from more than 60 sources.
The episode, first detailed in a widely syndicated piece by journalist Heather Stewart under the headline “World leaders must wise up to threat of cyber-attacks or rogue fridges will be least of their worries,” has become shorthand for a bigger argument playing out among the people who run the global economy: AI-enabled cyberattacks are no longer a future risk to model. They are a present-tense operational hazard, and the institutions responsible for financial stability are not moving fast enough to catch up.
Don't miss new tech stories on Google
Add TrendinTech once in the Google app and our stories appear in your news suggestions.
IMF Sounds the Alarm From Bangkok
The IMF-World Bank Annual Meetings typically generate headlines about growth forecasts, debt sustainability and currency policy. This year, according to the Stewart report circulated through newsmart.ch and other aggregators, cyber risk pushed its way into the same conversations as inflation and interest rates. The framing from Georgieva’s remarks was blunt: global cooperation on cybersecurity looks unlikely even as artificial intelligence raises the odds and the cost of digital fraud, at precisely the moment when protecting the financial system requires more coordination, not less.
That is a notable shift in tone for an institution that usually confines itself to fiscal and monetary territory. The IMF has spent years publishing research on cyber risk to banks and payment systems, but putting a specific, almost absurd-sounding incident, hacked refrigerators, in front of the world’s top economic officials signals that the Fund wants cyber risk treated as a mainstream macroeconomic concern rather than a niche IT problem for chief information security officers to handle quietly.
Georgieva’s broader point, as relayed in the coverage, is that the tools attackers now have access to, generative AI for crafting convincing phishing lures, automated vulnerability scanning, and AI-assisted exploit development, have compressed the time between discovering a weakness and weaponizing it. For an institution that spends its time thinking about systemic risk, that compression is the real story: a single exploited vulnerability in an unglamorous piece of industrial equipment can now cascade into supply chain losses within hours rather than weeks.
The Fridge Hack That Made Finance Chiefs Pay Attention
The incident itself took place in France, where attackers reportedly gained access to refrigeration controls at supermarket chains. Once inside those systems, they were able to push internal temperatures to around 50 degrees Celsius, well beyond the range needed to keep perishable stock safe. The result was spoiled food that had to be discarded, and in secondary coverage, reports of fires at affected sites, though the exact financial losses, the number of stores involved, and the identity of the attackers have not been independently confirmed.
This site covered the incident in depth when it first broke, including the discovery that a known flaw in refrigeration vendor Danfoss equipment had reportedly sat exposed for roughly 63 days before attackers exploited it, and the subsequent finding that the breach exposed operational technology risk across three separate equipment vendors. French authorities opened a formal investigation that, as last reported, had expanded to look at roughly 700 affected stores. The original breach, where temperatures spiked and stock was lost, is detailed in our earlier report on the French supermarket refrigeration hack.
What makes the incident useful as a talking point in Bangkok is precisely how unglamorous it is. Nobody budgets emergency funding to defend a walk-in cooler. Refrigeration controllers are not treated the way banks treat core payment rails or the way governments treat power grids. Yet the French breach demonstrated that a compromised piece of industrial control equipment can disrupt retail operations at scale, destroy inventory, and generate real financial losses, all without anyone touching a line of banking code.
Why Operational Technology Keeps Getting Overlooked
Operational technology, the hardware and software that controls physical processes like cooling, manufacturing lines, and building systems, has historically lagged well behind corporate IT for patching discipline and network segmentation. Vendors ship equipment that is designed to run for a decade or more, often without the kind of over-the-air update pipeline that consumer software now takes for granted. That gap is exactly why a vulnerability can sit unexploited for months before someone notices, and exactly why OT has become an attractive target for attackers who want disruption rather than data theft.
Who Is Kristalina Georgieva and Why Her Warning Matters
Kristalina Georgieva has led the International Monetary Fund since 2019, overseeing the Fund’s response to the pandemic-era debt crisis, the inflation shock that followed, and a string of regional banking stresses. When she chooses to highlight a specific risk at the Annual Meetings, it tends to move up the agenda for finance ministries that look to the IMF for guidance on where to focus supervisory attention.
Her comments on AI-enabled cyberattacks fit a pattern the Fund has been building for several years: repeated warnings that financial institutions, insurers, and regulators are underpricing cyber risk relative to how quickly the threat is evolving. The French refrigeration case gave that warning a concrete, almost relatable example rather than an abstract one. It is one thing to tell central bankers that cyber risk is rising. It is another to point at a story about hacked fridges spoiling groceries and note that the same category of attack, applied to a payment processor or a clearing system, would not be a story about wasted food.
Why AI Changes the Math on Cyberattacks
The core argument behind the Bangkok remarks is about speed and scale, not just novelty. AI-enabled cyberattacks do not necessarily rely on brand-new attack techniques. Phishing, credential stuffing, and exploitation of unpatched industrial control systems have existed for years. What changes with AI is throughput: a single operator can now generate thousands of tailored phishing messages, probe networks for known vulnerabilities automatically, and iterate on malicious code faster than defenders can test and deploy patches.
That dynamic puts pressure on an already uneven playing field. Large banks and critical infrastructure operators in wealthy economies tend to have mature security operations centers. Mid-sized retailers, regional utilities, and operators in emerging markets often do not. If AI tools make attacks cheaper to launch at scale, the actors least equipped to defend themselves become disproportionately exposed, which is precisely the kind of unevenly distributed risk that tends to worry an institution like the IMF, whose mandate includes financial stability across its full membership, not just its wealthiest members.
From Refrigeration Units to Financial Systems: The Connected-Risk Problem
The reason a supermarket cooling system ended up in a conversation about financial stability comes down to interconnection. Modern retail, logistics, and payments infrastructure are tightly linked. A retailer that loses perishable inventory faces direct losses, but also faces knock-on effects: insurance claims, supply chain disruption with upstream distributors, and in aggregate, pressure on consumer price indices if the disruption is widespread enough. None of that requires an attacker to touch a bank directly.
Insurers are the clearest transmission channel. Cyber insurance underwriters price policies based on historical loss data, and an attack pattern that moves from stealing data to physically damaging goods and equipment changes the loss model in ways insurers have not fully priced in yet. If physical-damage cyber claims become common across retail, manufacturing, and logistics, insurers either raise premiums sharply or pull back coverage, both of which ripple into the broader economy in ways that eventually land on a central banker’s desk.
Historical Context: Cyberattacks That Already Rattled Markets
The Bangkok warning did not emerge from nowhere. Financial regulators have been building toward this moment for years, watching a steady drumbeat of incidents that blurred the line between cybersecurity and financial stability. Ransomware attacks on hospital networks, payment processors, and shipping companies have already demonstrated that digital disruption translates directly into measurable economic loss. Crypto markets, which operate with less regulatory scaffolding than traditional banking, have offered some of the starkest examples: this site reported on a hack that drained $86 million from crypto holders earlier this year, prompting public warnings from industry figures about custody risk.
What distinguishes the current moment from earlier cyber scares is the breadth of targets. Attacks are no longer concentrated on obvious high-value targets like banks and exchanges. Healthcare providers, retailers, and now industrial refrigeration systems have all shown up in recent incident reports, a pattern consistent with attackers probing for the weakest link in a given supply chain rather than attacking the strongest point directly.
Market and Industry Reaction
Markets did not move sharply on the back of Georgieva’s comments, which is itself telling. Cyber risk continues to be treated by most investors as a tail risk rather than a priced-in factor, even as regulators and multilateral institutions escalate their language. That gap between official rhetoric and market pricing is a recurring theme in financial stability reports: officials warn, insurers quietly raise premiums, and public equity markets largely shrug until a specific company discloses a material incident. Commentary platforms that track policy chatter, including The Forge on commons.now, picked up the Bangkok remarks within hours, a sign of how quickly the warning spread even without an immediate market reaction to match it.
Within the cybersecurity industry itself, the reaction has been more immediate. Vendors that sell operational technology security, network segmentation tools, and industrial control system monitoring have used the French incident as a selling point in customer conversations, according to the pattern of coverage tracked by sternit.de’s ongoing hacker-focused news feed. Expect vendor marketing built around OT visibility and AI-driven threat detection to lean heavily on the fridge hack as a case study for the rest of 2026.
The Global Cooperation Gap
The most pointed part of the Bangkok message was not really about AI or fridges. It was about the absence of coordinated global policy. Georgieva’s framing, as relayed through multiple aggregators covering the meetings, suggested that cooperation between governments on cyber risk looks unlikely even as the threat grows, a gap that leaves the financial system exposed to attacks that do not respect national borders.
That gap is structural, not accidental. Cybersecurity regulation sits at the intersection of national security, trade policy, and financial supervision, three domains that rarely move at the same speed or share the same incentives. A country with a large domestic tech industry has different interests than one that imports most of its critical infrastructure equipment. A central bank worried about payment system resilience has different priorities than a trade ministry worried about export controls on dual-use technology. The IMF, which has convening power but no enforcement authority over cybersecurity policy, can highlight the risk, but it cannot force the European Union, the United States, and emerging-market governments to align on a shared framework.
How Governments Are Responding, Region by Region
Even without full coordination, individual governments are moving on their own tracks. The European Union has leaned on export controls and sanctions as one lever, expanding restrictions that now cover roughly 1,600 measures targeting chips and drone components tied to Russia, an approach aimed at supply chain security rather than domestic OT resilience directly, but part of the same broader effort to harden technology infrastructure against state-linked disruption.
In the United States and the United Kingdom, the regulatory conversation has focused more on critical infrastructure patching obligations and vendor accountability. Zero-day vulnerabilities in widely deployed enterprise software remain a persistent entry point for attackers: this site’s recent coverage of a flaw in Ivanti Connect Secure that let attackers chain three separate bugs to gain root access is one example of the kind of vulnerability chain that keeps showing up across sectors, from enterprise VPNs to industrial controllers.
The Enforcement Problem
Even where rules exist on paper, enforcement lags. Many jurisdictions require critical infrastructure operators to report incidents, but reporting requirements do not automatically translate into faster patching or better network segmentation. Fines for noncompliance are often small relative to the cost of a full OT security overhaul, which means operators frequently treat compliance as a paperwork exercise rather than a forcing function for real investment, a dynamic that regulators in Brussels, Washington and London have each acknowledged in various forms without fully solving.
Vendors and Operators Scramble to Patch Operational Technology
In the weeks following the French refrigeration breach, equipment vendors and retailers moved to audit their own exposure. The investigation into the French case, which by the last public update had grown to cover roughly 700 stores, reflects how far a single exploited vulnerability can spread once attackers understand how a vendor’s equipment is deployed across an entire retail chain rather than a single location.
Security teams at retailers outside France are reportedly conducting their own audits of refrigeration, HVAC, and other building-control systems, treating the French case as a wake-up call rather than an isolated incident. That is consistent with how OT security incidents tend to play out: a breach at one operator triggers a wave of defensive spending across the entire sector that uses the same class of equipment, often more effective at driving investment than years of regulatory warnings.
2026 Critical Infrastructure and OT Incident Timeline
The French fridge hack did not happen in a vacuum. It landed in a year that has already produced a string of incidents spanning operational technology, enterprise networking, and financial custody. The table below lines up the major cases referenced in this story.
| Incident | Sector | Reported Impact | Status |
|---|---|---|---|
| French supermarket refrigeration hack | Retail / OT | Cooling units hit roughly 50°C, spoiling stock | Investigation ongoing, scope expanded to about 700 stores |
| Danfoss equipment vulnerability | Industrial controls (OT vendor) | Flaw reportedly sat exposed for 63 days before exploitation | Patched after disclosure |
| Ivanti Connect Secure zero-day | Enterprise VPN / network access | Attackers chained three bugs to reach root access | Vendor patches issued |
| Ledger hardware wallet hack | Crypto custody / finance | Roughly $86 million drained from affected holders | Industry warnings issued, exact scope still being assessed |
Global Policy Posture Comparison
Different institutions are approaching the AI-cyber-financial risk nexus from different angles, and none of them currently has the authority to set a single global standard. The comparison below is based on the public positions and actions each body has taken so far in 2026.
| Body / Region | Stated Position | Recent Action | Main Challenge |
|---|---|---|---|
| IMF | Warns AI is raising systemic risk to financial stability | Raised the issue publicly at the Bangkok Annual Meetings | No enforcement authority over national cybersecurity policy |
| European Union | Treats supply chain security as a trade and sanctions matter | Expanded sanctions covering around 1,600 measures on chips and drone parts tied to Russia | Fragmented implementation across member states |
| United States / United Kingdom | Focuses on critical infrastructure patching and vendor accountability | Continued enforcement around enterprise software zero-days such as Ivanti Connect Secure | Reporting rules exist, but enforcement of remediation lags |
| Private sector / insurers | Treats cyber-physical damage as an emerging, underpriced risk | Vendors marketing OT visibility and AI-driven detection tools | Loss models have not caught up to physical-damage claims |
What Comes Next: Five Predictions
- Expect the IMF to publish a more detailed financial stability assessment of AI-enabled cyber risk in the coming months, building on the informal warning delivered in Bangkok rather than leaving it as a single speech.
- Cyber insurers will start separating physical-damage cyber coverage from data-breach coverage as a distinct product line, since the loss profiles behind an incident like the French fridge hack differ sharply from a typical data theft claim.
- Operational technology vendors supplying refrigeration, HVAC, and building controls will face pressure from large retail customers to publish faster patch timelines, following the pattern already seen after the Danfoss disclosure.
- Government coordination on cyber policy will remain fragmented through the rest of 2026, with the EU, US, and UK continuing to act through separate sanctions, enforcement, and disclosure regimes rather than a unified framework.
- More retailers and logistics operators will disclose OT security audits triggered directly by the French case, treating it as the reference incident the way earlier industries treated major ransomware outbreaks.
What This Means for Businesses and Consumers
For businesses, the practical takeaway from Bangkok is that operational technology can no longer sit outside the normal cybersecurity budget conversation. Refrigeration controllers, HVAC systems, and other building-automation equipment have historically been managed by facilities teams rather than security teams, often running on outdated firmware with minimal network segmentation from the rest of the corporate network. The French case shows what happens when that gap gets exploited: physical losses, operational downtime, and reputational damage that a purely IT-focused security program would not have caught.
For everyday consumers, the connection to a hacked fridge might feel abstract, but the chain runs fairly directly: disrupted supply chains raise costs, insurers pass higher premiums on to the businesses they cover, and those businesses pass costs on to shoppers. It is a slow, indirect version of the same mechanism that makes the IMF care about cyber risk in the first place. A warning delivered to finance ministers in Bangkok about rogue refrigerators is, underneath the odd framing, a warning about who ends up paying when systems nobody thought to defend get attacked anyway.
Frequently Asked Questions
What did Kristalina Georgieva actually warn about in Bangkok?
She told attendees at the IMF-World Bank Annual Meetings that AI is increasing the risk and reach of cyberattacks, and that global cooperation on addressing that risk looks unlikely even as the threat to the financial system grows, according to reporting on the meetings.
Why did the IMF bring up a supermarket fridge hack at an economic summit?
The French refrigeration breach, where hackers reportedly pushed cooling units to around 50 degrees Celsius and spoiled food, was used as a concrete example of how an attack on unglamorous operational technology can still generate real financial losses and systemic risk.
Has the French supermarket fridge hack been fully investigated?
French authorities opened an investigation that had expanded to cover roughly 700 stores as of the last public update. The exact financial losses, number of affected fridges, and identity of the attackers remain unconfirmed.
Is AI actually making cyberattacks worse, or is this overstated?
AI tools lower the cost and raise the speed of common attack techniques like phishing and automated vulnerability scanning. That does not necessarily introduce brand-new attack types, but it does let attackers operate at a scale that is harder for defenders to keep up with, which is the core of the IMF’s concern.
Who is responsible for securing operational technology like refrigeration systems?
Responsibility is typically split between the equipment vendor, which must patch known flaws, and the operator, usually a facilities or operations team rather than a dedicated security team, which must apply those patches and segment the equipment from the broader network.
Will global leaders agree on a unified cybersecurity policy anytime soon?
Current signals suggest no. Cybersecurity policy remains split across national security, trade, and financial supervision agencies with different incentives, and the IMF has no enforcement authority to force alignment across its member countries.
What should businesses do in response to this warning?
Security teams are being encouraged to extend audits beyond traditional IT systems to cover building automation, refrigeration, and other operational technology, and to work with insurers on how physical-damage cyber incidents are covered under existing policies.
Where can I read more about the original French fridge hack incident?
Earlier coverage detailed the initial breach, the exposed Danfoss vulnerability, and the operational technology risk it revealed across multiple vendors.
Related Coverage
Rachel Kowalski
Rachel Kowalski is the Cybersecurity Analyst at TrendinTech, where she covers vulnerabilities, ransomware, supply chain attacks, nation-state operations and the security rules shaping organizations in the United States and Europe. She writes to make risks and countermeasures understandable to people who are not specialists.
All stories by Rachel Kowalski (254)