Saudi Engineer, 35, Charged in OpenAI Bug Case [2026]
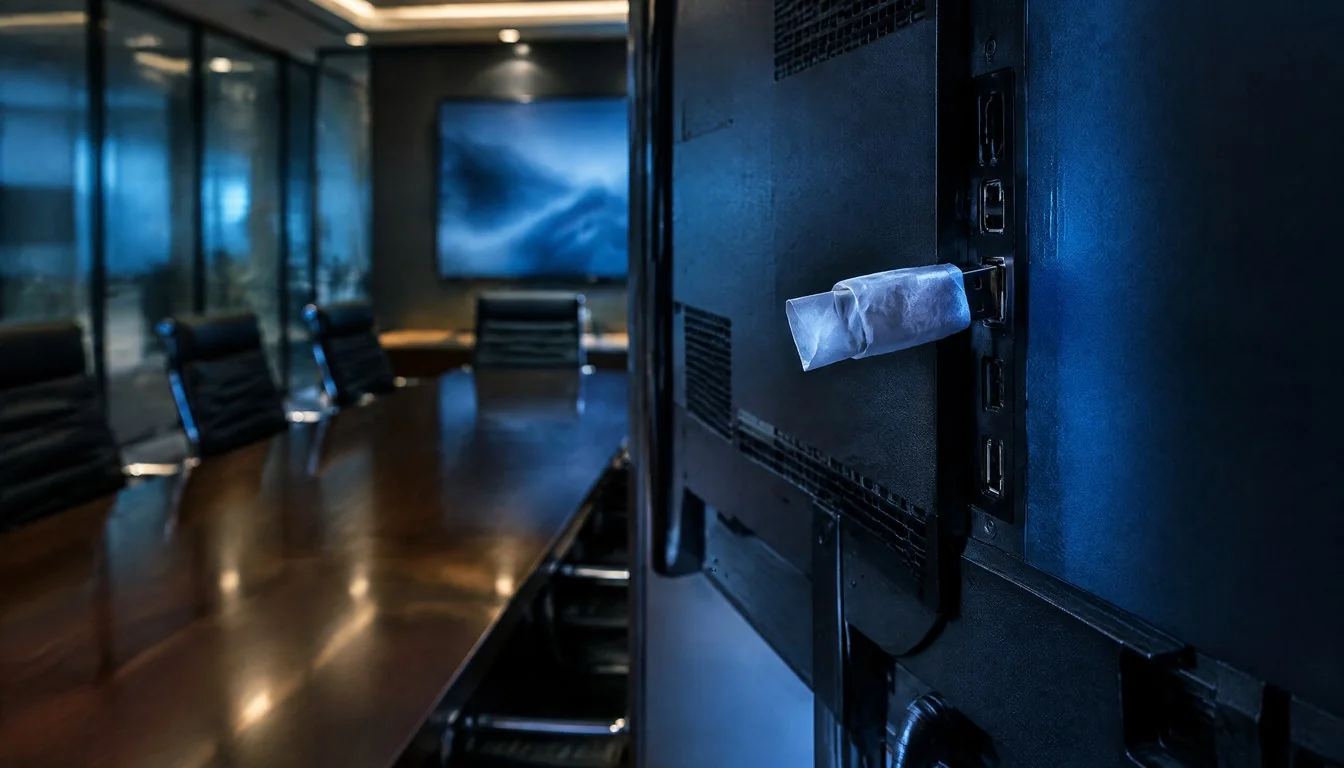
A Saudi national who worked as an engineer at OpenAI has been arrested and charged with planting a hidden audio recording device inside an executive conference room at the company’s San Francisco headquarters. The U.S. Department of Justice announced the case on October 13, 2026, describing a device wrapped in toilet paper, plugged into the back of a television over a USB port, and left running for days before anyone noticed.
The suspect, identified by federal prosecutors as Abdulrahman Alfozan, 35, was arrested on October 9 and made his initial appearance in federal court on October 13. He faces a charge under the federal wiretapping statute for using or attempting to use an electronic, mechanical, or other device to intercept oral communications. The case has moved fast by the standards of corporate espionage prosecutions: discovery, internal investigation, an FBI referral, an arrest, and a court appearance, all within about two weeks.
Don't miss new tech stories on Google
Add TrendinTech once in the Google app and our stories appear in your news suggestions.
What Happened Inside OpenAI’s Executive Conference Room
According to the Department of Justice, OpenAI personnel discovered the device, which prosecutors labeled “Recording Device 1” in the criminal complaint, on or about September 30, 2026. It was found inside an executive conference room in one of OpenAI’s San Francisco buildings, inserted into a USB port on the back of a television in the room. The device had been concealed in toilet paper, a detail that stood out across nearly every outlet that covered the story, including The Verge and the BBC.
Federal prosecutors say the device was installed on or about September 28, 2026, meaning it sat in place for roughly 48 hours before anyone at OpenAI spotted it. The company determined that Alfozan did not have authorized access to that executive conference room, a detail the Justice Department highlighted as central to the intrusion claim. The contents stored on the device were encrypted, and nothing in the public record so far indicates that investigators have recovered or decrypted any audio that was actually captured.
That last point matters for how the story should be read. The alarming part of this case is the planning and the physical breach of a restricted room, not a confirmed leak of a specific OpenAI meeting. No outlet covering the case, including CNBC, has reported that any recorded conversation was recovered or made public. The charge itself covers the act of intercepting or attempting to intercept, which does not require prosecutors to prove the device actually captured usable audio.
Who Is Abdulrahman Alfozan
Abdulrahman Alfozan is a 35-year-old national of the Kingdom of Saudi Arabia who worked at OpenAI as an engineer. The Justice Department’s announcement did not detail his specific team or project assignment, and OpenAI has not published that information publicly either. What is established is that he was an OpenAI employee at the time of the alleged intrusion, and that the company determined he lacked authorization to be inside the executive conference room where the device turned up.
Alfozan’s arrest came four days after OpenAI’s internal team flagged the device to federal authorities. He is currently facing a single charge tied to the interception statute, and no outlet has reported a conviction, a plea, or an outcome beyond the initial court appearance. It is worth being precise about his legal status given how fast corporate security stories tend to get flattened into something more dramatic than what has actually been proven in court. As of this writing, Alfozan has been charged, not convicted, and the allegations against him remain to be tested at trial or resolved through a plea.
How OpenAI Says It Caught the Device
OpenAI’s own account of the discovery adds a detail that is likely to get as much attention as the toilet paper wrapping: the company says it used its own AI models to help trace the device back to the person who planted it. An OpenAI spokesperson described the process this way, in a statement reported by multiple outlets: the company used its models to understand the device and where it had come from, identifying that a specific employee had planted it a few days earlier.
That is a notable claim for a company whose entire business is selling AI systems as tools for solving exactly this kind of analytical problem. If OpenAI’s internal security team actually ran its own models against building logs, badge data, or network traffic to identify a single employee out of thousands within days, that is a real-world demonstration of the kind of internal threat detection that security vendors have been promising enterprises for years. It also raises the obvious question of what records OpenAI’s systems have access to and how routinely the company runs this kind of internal analysis on its own staff, a question OpenAI has not addressed publicly.
Once OpenAI identified the employee, the company reported the discovery to the FBI, which opened an investigation that led to Alfozan’s arrest roughly nine days after the device was first found. That is a fast turnaround for a federal case involving physical evidence, encrypted data, and an international angle, which suggests OpenAI’s internal work gave investigators a running start rather than leaving them to build the case from scratch.
The FBI’s Statement and the “Superintelligence” Framing
FBI Director Kash Patel issued a public statement tying the arrest to the Bureau’s broader counterintelligence mission around AI companies. Patel said Alfozan “allegedly concealed a covert recording device inside his employer’s executive conference room to secretly capture sensitive communications.” The statement frames the case as part of a pattern the FBI is watching closely: attempts to steal sensitive AI research and strategy from the handful of companies racing to build the most capable models.
Some reporting on Patel’s remarks, including coverage that referenced “superintelligence technology” as the apparent target of the alleged surveillance, reflects language the FBI has used to describe why AI labs like OpenAI are now treated as high-value targets for espionage, on par with defense contractors or chipmakers. Nothing in the confirmed record identifies which specific research, product plans, or deals the device was meant to capture. The company has not said what was being discussed in that conference room around the date the device was installed, and no outlet has published those details either.
Why This Case Lands Differently Than a Typical Data Breach
Most of the security stories coming out of the AI industry this year have involved remote attacks: credential theft, prompt injection, model extraction, or distillation attempts aimed at copying a frontier model‘s behavior without the underlying weights. Anthropic’s recent work cutting distillation attacks by 99 percent is a good example of the kind of threat AI labs have spent the most public effort defending against: someone outside the company trying to extract value from a model over the network.
The Alfozan case is different because the threat came from inside the building, from someone with a badge and a desk. Physical access controls, not firewalls or rate limiters, are what failed here, at least for the roughly 48 hours between installation and discovery. That distinction matters for how every AI lab, not just OpenAI, should be thinking about security budgets. A company can spend enormous sums on red-teaming its models and securing its API endpoints while leaving a conference room where the actual humans making decisions about those models talk unprotected against someone walking in with a device wrapped in toilet paper.
It also lands at a moment when OpenAI employees have been under a particular kind of scrutiny. The company has been navigating public debate over how honestly its own workforce represents its use of AI tools internally, a theme explored in the reporting on performative AI use among employees earlier this year. An insider threat case adds a different, more serious dimension to questions about who inside these companies can be trusted with access to sensitive spaces and conversations.
Historical Context: Corporate Espionage in the AI Race
Corporate espionage is not new to Silicon Valley. Trade secret theft cases involving self-driving car technology, chip designs, and search algorithms have shown up in federal court for more than a decade. What is new is the stakes attached to a single conference room conversation at a company like OpenAI. When the product is a search algorithm improvement, a leaked roadmap is embarrassing. When the product is reportedly described internally as superintelligence research, a leaked roadmap can shift how governments, competitors, and investors value the entire company.
That is part of why the FBI’s language in this case reads differently than it would have five years ago. AI labs are now discussed in the same breath as defense contractors and critical infrastructure operators for counterintelligence concern. OpenAI’s own structure reflects that shift: the company has increasingly described itself in safety and security filings as building frontier technology with national security implications, not simply a consumer software product. That framing changes how seriously an alleged bugging incident gets treated by federal law enforcement, and it explains why the FBI director personally commented on an arrest involving a single device and a single employee.
The case also arrives alongside a string of other security incidents across the tech sector this year. Ledger’s confirmed hardware implant case showed that physical tampering with devices remains a live threat vector even as most security spending goes toward software defenses. The ShinyHunters arrests covered in the FBI’s pursuit of a second suspect tied to that group show federal agencies are increasingly willing to move quickly on tech-sector cybercrime cases once a company hands over a clean internal investigation.
Legal Exposure Under the Federal Wiretapping Statute
The charge against Alfozan falls under the federal law that prohibits intentionally intercepting, attempting to intercept, or procuring another person to intercept an oral communication using an electronic, mechanical, or other device. That statute does not require prosecutors to prove a successful interception took place. Attempting to intercept, or taking substantial steps toward doing so, can be enough to support a charge, which is one reason the encrypted and apparently unread contents of the device do not weaken the government’s case the way they might in a simpler theft prosecution.
What happens next in the courtroom is not yet public. Alfozan has made only an initial appearance, and no outlet has reported a plea, bail conditions, or a trial date. Given his nationality, questions about any immigration or visa proceedings running in parallel with the criminal case are likely to surface, but nothing in the confirmed reporting addresses that either. The case bears watching for how federal prosecutors handle digital evidence that was never successfully decrypted, since that detail could shape pretrial motions around what the government can and cannot prove happened once the device was live.
Market and Reputational Impact for OpenAI
OpenAI is a private company, so there is no stock price to move on a story like this the way a public company’s shares might react to a breach disclosure. But reputational stakes for a company sitting at the center of the AI investment boom are arguably higher than a quarterly earnings miss. OpenAI has spent the past two years positioning itself as the trusted center of gravity for enterprise AI deployment, cloud partnerships, and government relationships. An insider planting a hidden recording device in the room where executives talk is the kind of story that competitors, partners, and potential regulators will not let fade quickly.
At the same time, OpenAI’s quick internal detection and fast handoff to the FBI gives the company a counter-narrative to lean on. Being the target of an attempted bugging is not itself a story that reflects poorly on security practices if the company can show it caught the intrusion within roughly 48 hours and built enough of a case internally to help federal investigators move to an arrest within nine days. Enterprise customers evaluating whether to trust OpenAI with sensitive workloads will likely weigh that response time as evidence the company’s internal security operation functions, even if the fact that an unauthorized device reached an executive conference room at all remains the more uncomfortable half of the story.
Comparing OpenAI’s Response to Other industry reporting Threat Cases
The table below places the Alfozan case alongside other publicly disclosed insider-threat and physical-security incidents at major technology companies over the past several years, based on details confirmed in public reporting and court filings at the time each case became public.
| Case | Company | Alleged Method | Detection Time | Outcome Status |
|---|---|---|---|---|
| Alfozan recording device | OpenAI | Hidden audio device in USB TV port, executive conference room | About 48 hours after installation | Charged, awaiting trial |
| ShinyHunters data theft cases | Multiple enterprise SaaS platforms | Credential theft and data exfiltration | Varies by victim, often weeks | Arrests made, prosecutions ongoing |
| Ledger hardware implant | Ledger and affected hardware wallet supply chain | Physical hardware tampering | Disclosed after theft losses mounted | Confirmed, losses spreading across Europe |
| Self-driving trade secret cases (historical) | Various autonomous vehicle companies | Downloaded files before departure to competitor | Discovered post-departure | Settled or resolved through civil and criminal tracks |
The pattern across these cases is that detection speed varies enormously depending on whether the intrusion is physical, digital, or a hybrid of both. A physical device inside a conference room is, in some ways, easier to find once someone looks, which may explain why OpenAI’s internal team closed the loop in days rather than the weeks or months typical of credential-based breaches.
Timeline of the OpenAI Recording Device Case
| Date | Event |
|---|---|
| September 28, 2026 | Device allegedly installed in OpenAI executive conference room, according to federal prosecutors |
| September 30, 2026 | OpenAI personnel discover the device inserted into a television’s USB port |
| Following days | OpenAI says it used its own AI models to trace the device to a specific employee |
| Unspecified date before October 9 | OpenAI reports the discovery to the FBI |
| October 9, 2026 | Abdulrahman Alfozan is arrested |
| October 13, 2026 | Department of Justice announces charges; Alfozan makes initial federal court appearance |
What This Means for AI Industry Physical Security Practices
Every major AI lab is now operating with the understanding that the inside of an executive conference room is a target, not just the model weights sitting on a server. OpenAI’s case is likely to push competitors including Anthropic, Google DeepMind, and Meta’s AI research division to review who has unsupervised access to executive spaces, how often those rooms are swept for unauthorized devices, and whether USB ports on conference room televisions and displays should be physically disabled or monitored by default.
This is a cheap fix compared to the kind of security spending AI labs have already committed to protecting model weights and training infrastructure. A USB port lockdown policy or a scheduled room sweep costs a fraction of what these companies already spend on cybersecurity teams. The fact that it apparently was not standard practice at a company valued among the most important in the industry suggests physical security has lagged well behind digital security investment across the sector, not just at OpenAI specifically.
Predictions: Where This Story Goes From Here
Based on how similar federal cases have unfolded and the specific facts confirmed so far, here is how this story is likely to develop over the coming months.
- Expect OpenAI to tighten physical access controls across its San Francisco offices, including likely new policies around USB ports on conference room hardware and more frequent physical security sweeps, even if the company does not publicize the specific changes.
- Expect competing AI labs to quietly review their own executive conference room security in the coming weeks, given how closely the industry tracks security incidents at rival companies.
- Expect the FBI to continue publicly framing AI lab security incidents through a national security lens, given Director Patel’s direct statement on this case, which signals the Bureau sees AI company espionage as a priority area going forward.
- Expect Alfozan’s case to move slowly through pretrial proceedings over the coming months, with his legal team likely to challenge how prosecutors characterize an attempted interception when no recorded or decrypted content has been confirmed as captured.
- Expect scrutiny of how OpenAI’s internal investigation was conducted, including questions from employees and civil liberties advocates about what level of internal monitoring enabled the company to identify a specific employee within days of discovering the device.
What OpenAI Has Not Said
It is worth being clear about the boundaries of what has actually been confirmed, because stories like this tend to accumulate unverified detail as they spread. OpenAI has not disclosed which executives used that conference room, what topics were discussed around the date the device was installed, or what specific research or business plans might have been exposed if the device had functioned as intended. The company also has not detailed exactly how its AI models were used to trace the device to Alfozan, beyond the general statement that it used its models to understand the device and identify the employee responsible.
Similarly, nothing in the public record describes the device’s manufacturer, its storage capacity, or how it was meant to transmit or store recorded audio before someone presumably intended to retrieve it. The encryption on the device’s contents has not been broken, as far as any outlet has reported, meaning investigators may not know with certainty whether the device captured any audio at all before it was found.
Broader Implications for AI Talent and Trust
OpenAI, like its major rivals, has hired aggressively from a global talent pool to staff its research and engineering teams, including from countries across the Gulf region that have been investing heavily in AI partnerships and infrastructure. This case does not establish anything about the motivations behind Alfozan’s alleged actions, and no outlet has reported a connection to any government, competitor, or outside party seeking the information. Treating this as evidence of a broader pattern tied to any nationality or region would be an unsupported leap well beyond what prosecutors have alleged.
What the case does demonstrate, regardless of motive, is that the world’s most closely watched AI companies are now dealing with insider threat scenarios that look more like the ones faced by defense contractors and intelligence agencies than typical Silicon Valley startups. That shift in risk profile is likely to shape hiring, access control, and internal monitoring policy at OpenAI and across the industry for years, independent of how Alfozan’s individual case is ultimately resolved in court.
Frequently Asked Questions
Who is Abdulrahman Alfozan?
He is a 35-year-old Saudi national who worked as an engineer at OpenAI and has been charged by federal prosecutors with planting a hidden recording device in an executive conference room at the company’s San Francisco headquarters.
What exactly was found in OpenAI’s conference room?
OpenAI personnel found a device prosecutors called “Recording Device 1” concealed in toilet paper and inserted into a USB port on the back of a television inside an executive conference room, discovered on or about September 30, 2026.
Did the device actually record any conversations?
That has not been confirmed. The device’s contents were encrypted, and no outlet has reported that investigators successfully decrypted or recovered any recorded audio.
What charge is Alfozan facing?
He is charged with using or endeavoring to use an electronic, mechanical, or other device to intercept oral communications, a charge brought under the federal wiretapping statute. He has not been convicted of any crime.
How did OpenAI identify the suspect?
OpenAI said it used its own AI models to analyze the device and trace it back to a specific employee who had allegedly planted it a few days earlier, then referred the matter to the FBI.
When was Alfozan arrested?
Federal agents arrested him on October 9, 2026. He made his initial appearance in federal court on October 13, 2026, when the Department of Justice announced the case publicly.
What did the FBI say about the case?
FBI Director Kash Patel said Alfozan allegedly concealed a covert recording device inside his employer’s executive conference room to secretly capture sensitive communications.
Was Alfozan authorized to be in that conference room?
No. The Department of Justice said he was not authorized to access the executive conference room where the device was found.
Related Coverage
Daniel Okafor
Daniel Okafor is the Senior AI Reporter at TrendinTech, where he covers large language models, machine learning research and the practical use of artificial intelligence across business and government. He has a particular interest in evaluation: how models are benchmarked, where those benchmarks fail and what that means for the companies betting on them.
All stories by Daniel Okafor (355)